
Key facts
- Threat actors are actively exploiting CVE-2026-58115 in Siemens SIMATIC IoT2050 Advanced devices to plant remote command backdoors, according to VulnCheck.
- CVE-2026-58115 is a maximum-severity authentication bypass with a CVSS score of 10.0.
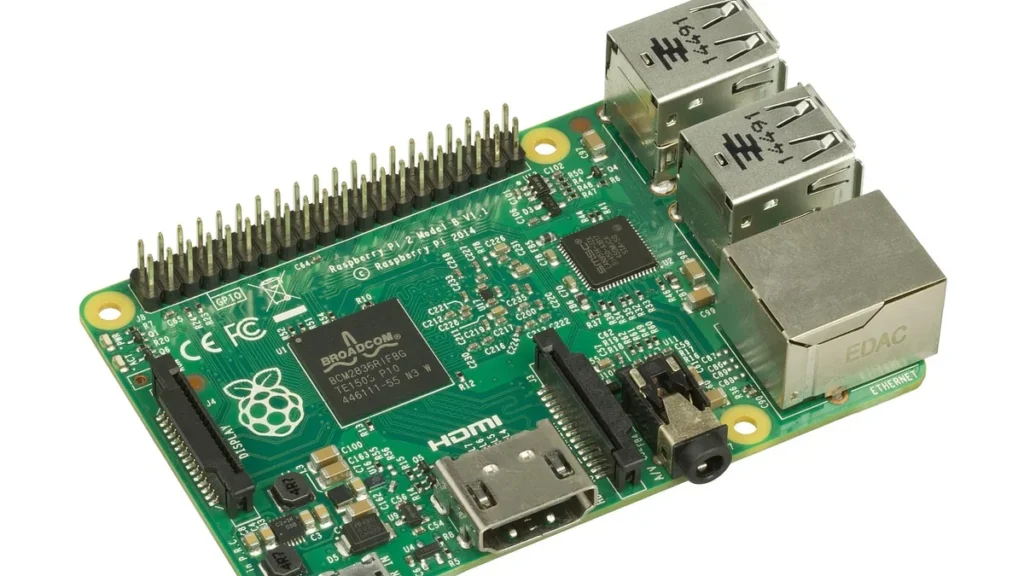
- The flaw involves missing authentication for the Node-RED HTTP interface on Siemens SIMATIC IoT2050 Advanced devices running Industrial OS with Node-RED installed.
- An unauthenticated attacker can exploit the flaw to build malicious Node-RED flows and run any code on the host with full privileges.
Attackers are exploiting CVE-2026-58115 (Common Vulnerabilities and Exposures), a critical authentication bypass in Siemens SIMATIC IoT2050 Advanced hardware, to plant remote command backdoors, VulnCheck said after spotting initial in-the-wild strikes on Oct. 30, 2026.
The flaw carries a CVSS (Common Vulnerability Scoring System) score of 10.0 and stems from missing authentication on the Node-RED HTTP interface of Siemens SIMATIC IoT2050 Advanced hardware running Industrial OS with Node-RED installed. An unauthenticated attacker can create malicious Node-RED flows and execute any code on the host with full privileges, including code running as root. The Node-RED HTTP management interface runs on port 1880, and Siemens rated the flaw 10.0 under CVSS 3.1 and CVSS 4.0 and described it as missing authentication for a critical function under CWE-306.
Siemens published its advisory in August 2026, and the CVE appeared on Aug. 11. VulnCheck had issued detections for the flaw three days before its sensors detected the initial in-the-wild hit. A single IP address carried out 16 attacks against the flaw between Oct. 30 and Nov. 1, 2026. Patrick Garrity, a VulnCheck researcher, said the request from the attacker constituted a complete exploit that launched a flow, executed it without delay, and pulled a binary from a server controlled by the attacker through three layers of encoding.
Attackers used wget inside a malicious flow to pull an AMD64 botnet binary from 85.215.73[.]250, saving it as /dev/shm/.b before execution, with curl available if wget did not work. The attackers then moved to a two-stage method that pulls a second script called wget.sh from that same server. Another request grabbed a payload called .sys_update from 45.194.90[.]57:38472 and wrote it to /tmp/.kworker to look like a kernel worker thread. The researchers failed to recover wget.sh or .kworker, so what those items do remains unknown, and some requests revealed an HTTP-in endpoint like /cmd tied by a function node to an exec node with addpay enabled, so commands could run later through a query parameter.
Garrity said the backdoor survives a reboot even when a memory-backed implant disappears. VulnCheck said the attacking IP address resides in Microsoft cloud infrastructure, appears to be in Brazil, and is a compromised or rented virtual machine instead of attacker-owned hardware. A single address logged 125 hits against eight distinct CVEs including Apache Solr, Gitea, MLflow and Joomla, which points to broad scanning rather than a targeted operation.
VulnCheck said the flaw does not appear in CISA’s Known Exploited Vulnerabilities catalog, although VulnCheck added CVE-2026-58115 to its own list. CISA enrichment data indicated no known exploitation one day after the CVE appeared and classified the flaw as automatable with total technical impact.
IoT2050 hardware commonly serves as a link between operational technology and higher-level IT systems, so attackers can use a compromised gateway as a stealth entry point, add it to a botnet, or use it as a foothold to move into adjacent networks. Installed IoT2050 gateways might not appear in standard IT asset inventories when operators outsource setup and administration, leaving vulnerable devices unpatched and unseen.
Node-RED provides password protection through adminAuth, but the affected Siemens devices do not require authentication on that interface. Garrity said two built-in nodes, an inject node and an exec node, make the flaw simple to weaponize, and linking one inject node to an exec node makes the flow run a command right after deployment with no further steps. Attackers send malicious flow JSON payloads using Node-RED’s exec node to trigger system commands through a POST request to the /flows endpoint.
The flaw affects firmware before V4.3.4.1, while the fix exists in Industrial OS versions 4.3.4.1 or later. Siemens recommends that affected devices move to Industrial OS V4.3.4.1 or later.
When immediate patching is impossible, Siemens advises removing Node-RED or hardening it with HTTPS and authentication for the editor, admin API, HTTP nodes and dashboard. VulnCheck says operators must verify that Node-RED admin pages cannot be reached from the internet and check flows for unauthorized exec nodes or HTTP endpoints. Axiom Cyber Research recommends strict network segmentation to keep IoT2050 Advanced devices isolated from public or internet-facing networks, and urges signature-based IDS/IPS rules to block unusual POST requests aimed at port 1880. Garrity told operators to confirm whether Node-RED is reachable from outside their network, apply available updates, and configure detections.
This campaign follows earlier attacks on internet-exposed OT and ICS (industrial control systems) gear, including incidents against refrigeration controllers in Europe and water systems across at least 12 US states during the summer. Garrity said old and new flaws across unrelated products point to opportunistic mass scanning rather than a targeted campaign.
Defenders should apply the available Industrial OS update immediately. For unpatched devices, remove Node-RED or harden its interfaces, isolate the gateway from public networks, and inspect flows for unauthorized exec nodes or HTTP endpoints.
Join the discussion