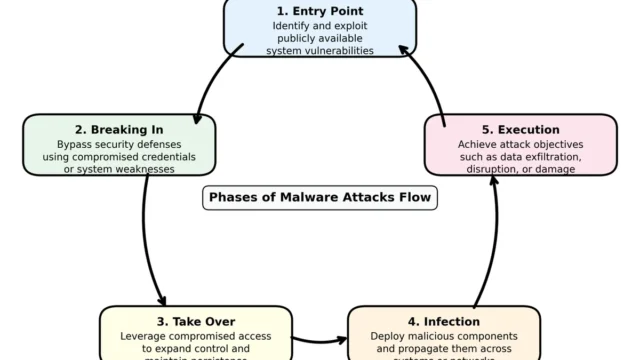
MITRE releases ATT&CK v20 with AI abuse, MFA bypass, water utility techniques
MITRE says the update broadens coverage of recent adversary activity and tradecraft.
threat actor APT nation-state espionage campaign botnet infrastructure C2 hosting
MITRE says the update broadens coverage of recent adversary activity and tradecraft.
Armory Castle began exploiting BeyondTrust zero-day CVE-2026-102764 on August 29, 2026.

ConnectWise disabled seven compromised application identities after attackers used them to authenticate across 173 Microsoft 365 tenants.
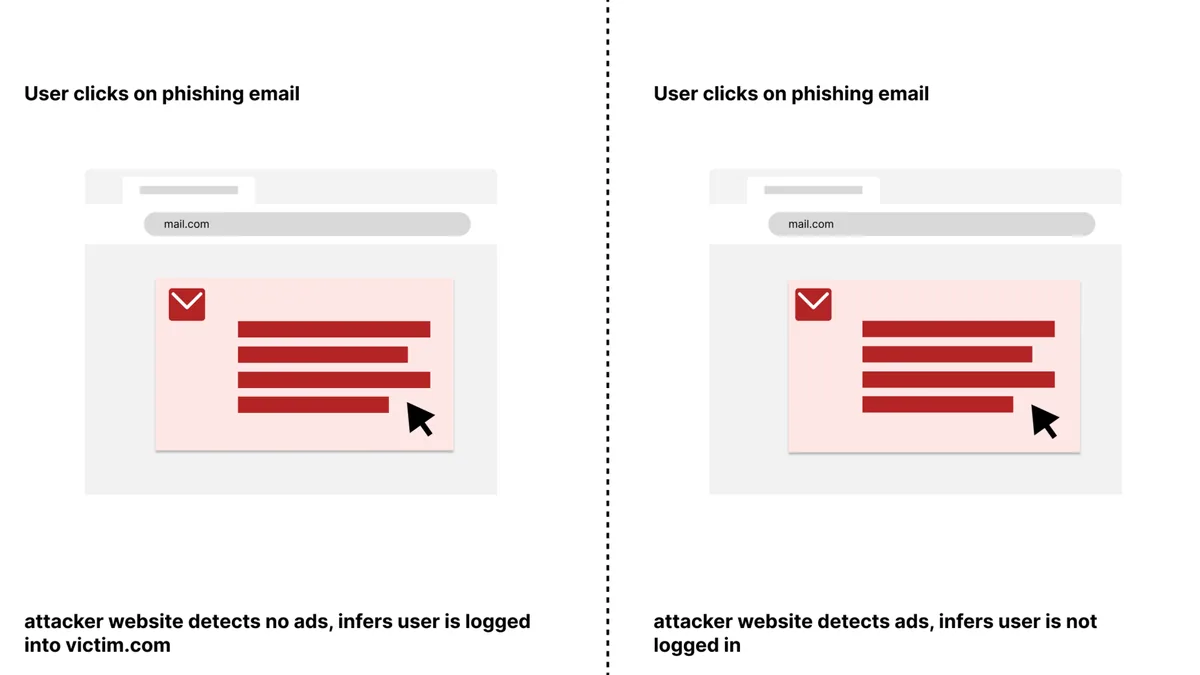
Darktrace notes the malware collects system data, captures screenshots, and the PowerShell script attempts to copy the Rust DLL into Microsoft Edge's installation folder and rename it dbghelp.dll.
The MALFEX campaign has used the package to deliver a loader that downloads encrypted shellcode from GitHub on Windows systems.
Huntress reported that attackers used the credential to get Microsoft Graph tokens from IP address 144.172.64.128 on October 15, 2026 between 06:13 and 08:34 UTC.

Google warns of continued targeting of edge devices as the group deploys webshells, backdoors and SOCKS5 tunneling after patch release

Citizen Lab confirms AdFection as the first zero-click spyware delivery method via ads, linked to 45 infected Al Jazeera devices between 2024 and 2025
The espionage group exploited CVE-2026-102764 to deploy custom malware, harvest credentials, and evade detection across enterprise networks, researchers say
Abdulrahman Alfozan, a 35‑year‑old Saudi engineer at OpenAI, was arrested last Friday on charges of intercepting communications after a hidden recording device was found in a San Francisco conference room

The operation, designated CL‑UNK‑1211, occurred between October 2025 and April 2026 and involved AI‑created payloads that held conversational comments and reasoning notes, showing LLM‑assisted code generation.
It focuses on water protection, resource handling, and energy systems across the CIS.