
Key facts
- Frontline Education disclosed a data breach affecting more than 1.3 million people, including K-12 school district staff and students.
- Criminals used a weakness in software supplied by another company to enter Frontline Education's systems on August 14, 2026.
- Frontline stated that August 15, 2026, was the final day of unauthorized activity.
- Frontline Central and School Health Management were the products holding the stolen information.
Criminals used a weakness in software supplied by another company to enter Frontline Education’s systems on August 14, 2026. Frontline Education disclosed a data breach affecting more than 1.3 million people, including K-12 school district staff and students. The company is based in Wayne, Pennsylvania, and sells K-12 administration software for recruiting, applicant tracking, onboarding, employee records, evaluations, absences, substitute management through Aesop, and district analytics. Its K-12 software also provides professional development tools plus district-level reporting and analytics covering operational, financial and student data.
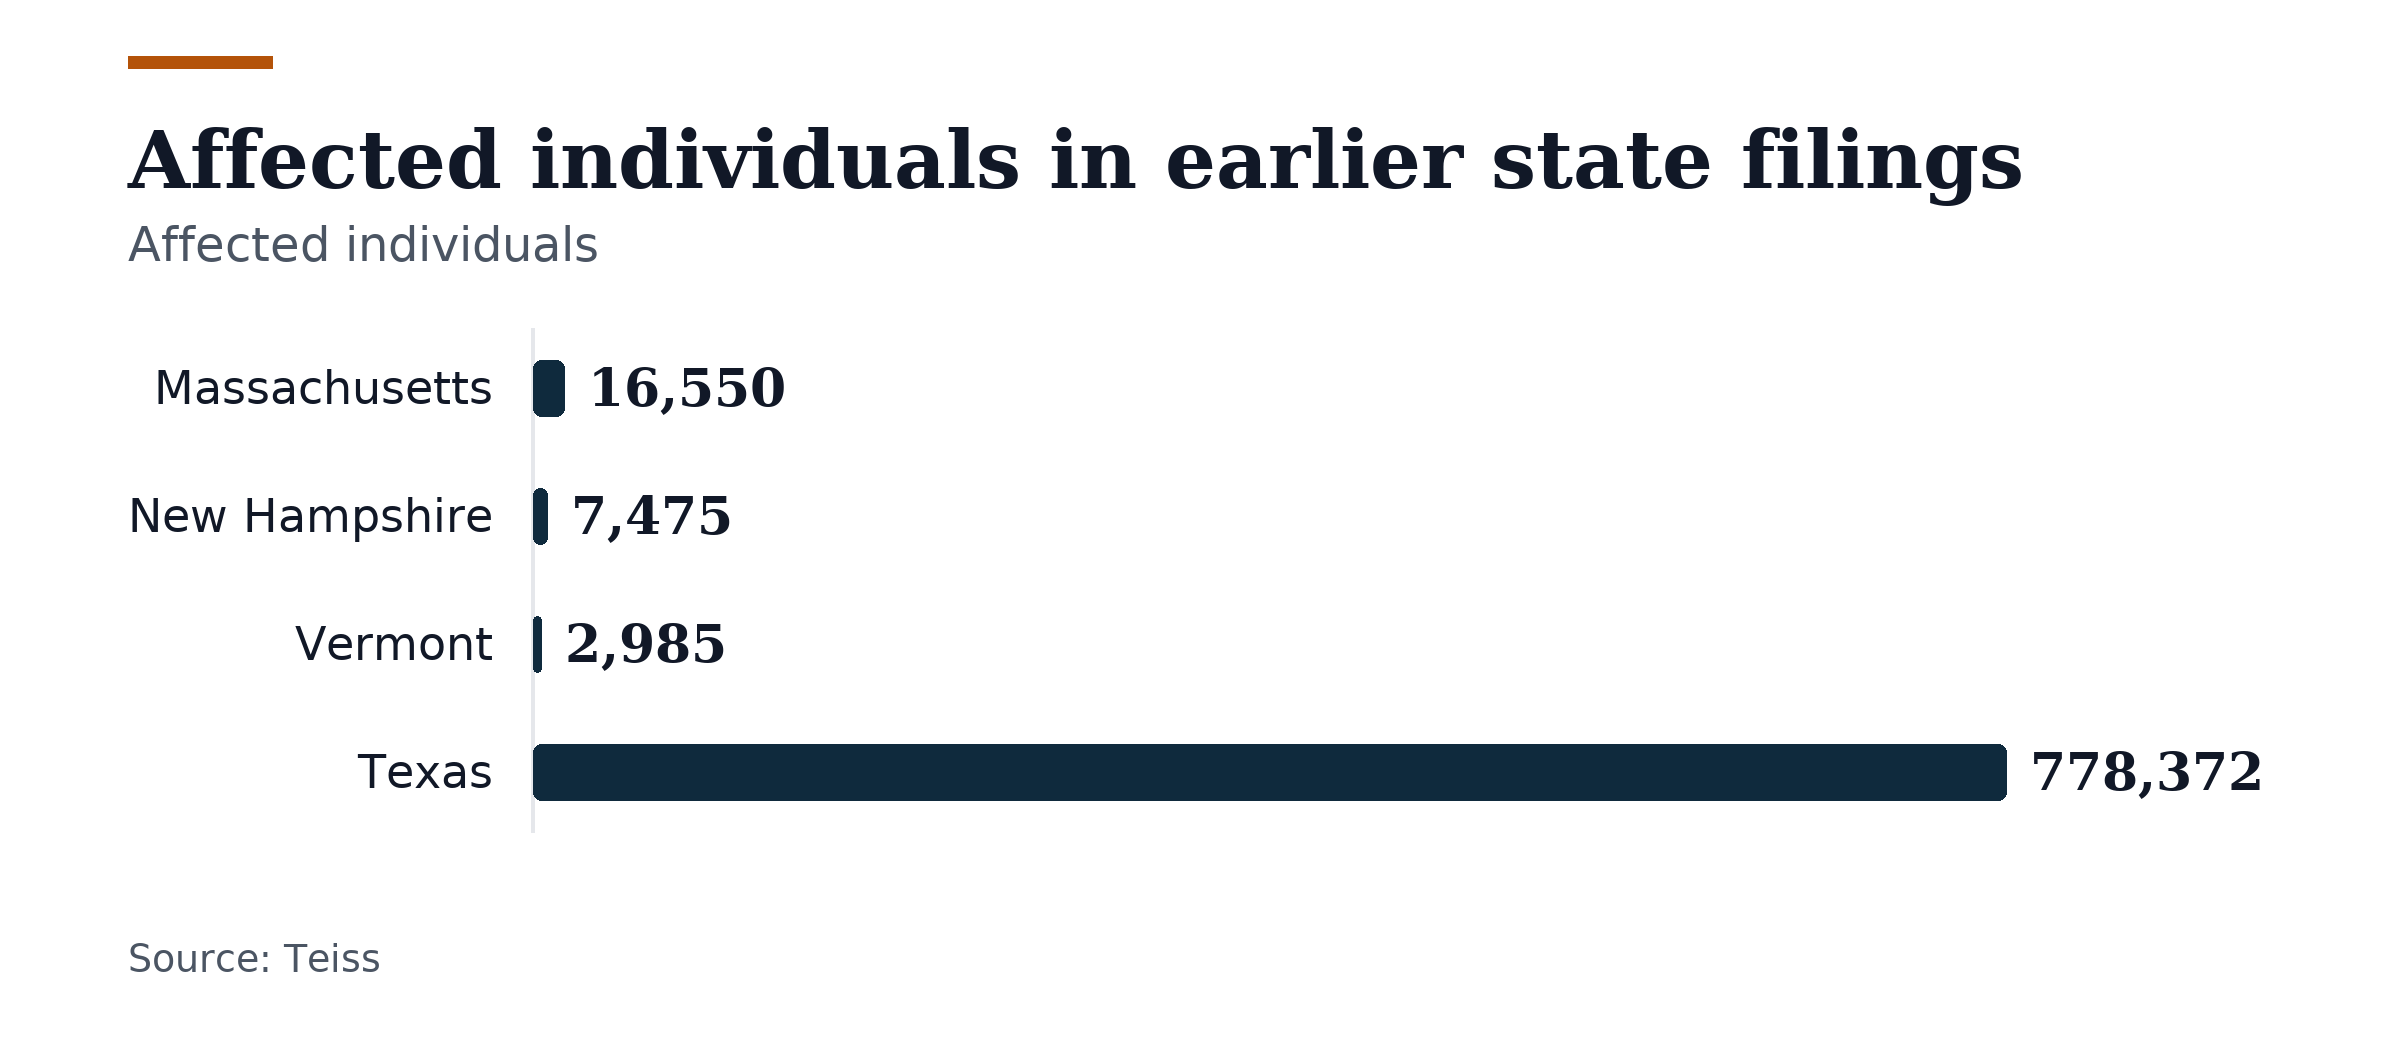
Frontline stated that August 15, 2026, was the final day of unauthorized activity, saying, “The last day of unauthorized activity was August 15.” State attorney general filings in Massachusetts, New Hampshire, South Carolina, Texas, and Vermont show 1,298,917 affected individuals, a confirmed victim count from state filings, though Frontline has not shared a total. The company also filed notices in California, Indiana, and Iowa, and possibly elsewhere, indicating additional state filings and suggesting the actual total is likely above 1.3 million, so the confirmed state-filing figure does not capture every affected individual. Earlier state-level filings counted 16,550 affected people in Massachusetts, 7,475 in New Hampshire, 2,985 in Vermont, and 778,372 in Texas, for a four-state total of 805,382.
As of October 29, 2026, no hacker group had claimed responsibility, and Frontline had not identified the attacker, the volume of data taken, or any ransom demand. Frontline used an independent cybersecurity firm to investigate and told law enforcement about the incident.
Potentially stolen details include names, Social Security numbers, dates of birth, and driver’s license numbers, categories of exposed personal information. Other exposed details potentially include passport numbers, other government ID numbers, Medicaid IDs, health insurance information, and Student IDs, categories of exposed personal information.
Frontline Central and School Health Management were the products holding the stolen information. The company fixed the flaw and strengthened its security monitoring controls as post-breach remediation steps. Frontline published a webpage with more information about the security incident. Affected adults in the United States get two years of complimentary credit monitoring and identity protection.
Qualifying minors receive free dark-web monitoring services, and Frontline offers minors no-cost cyber monitoring through TransUnion. TransUnion operates a dedicated call center to help eligible individuals enroll and ask questions. Frontline notified affected school districts and began alerting affected individuals by e-mail or letter. The company said it “has begun notifying individuals whose personal information was affected via email or by letter.”
Individual notices began going out on or about October 26, 2026. According to the company’s announcement, the letters and emails tell recipients what data was exposed and provide the TransUnion support line for enrollment and questions related to the incident.
Affected individuals should monitor credit reports, account statements, and benefit statements and report suspicious activity to police and state attorneys general as advised protective steps.
Join the discussion