
Key facts
- Frontline Education confirmed that attackers exploited a flaw in outside software to access sensitive information tied to K-12 school districts in August 2026.
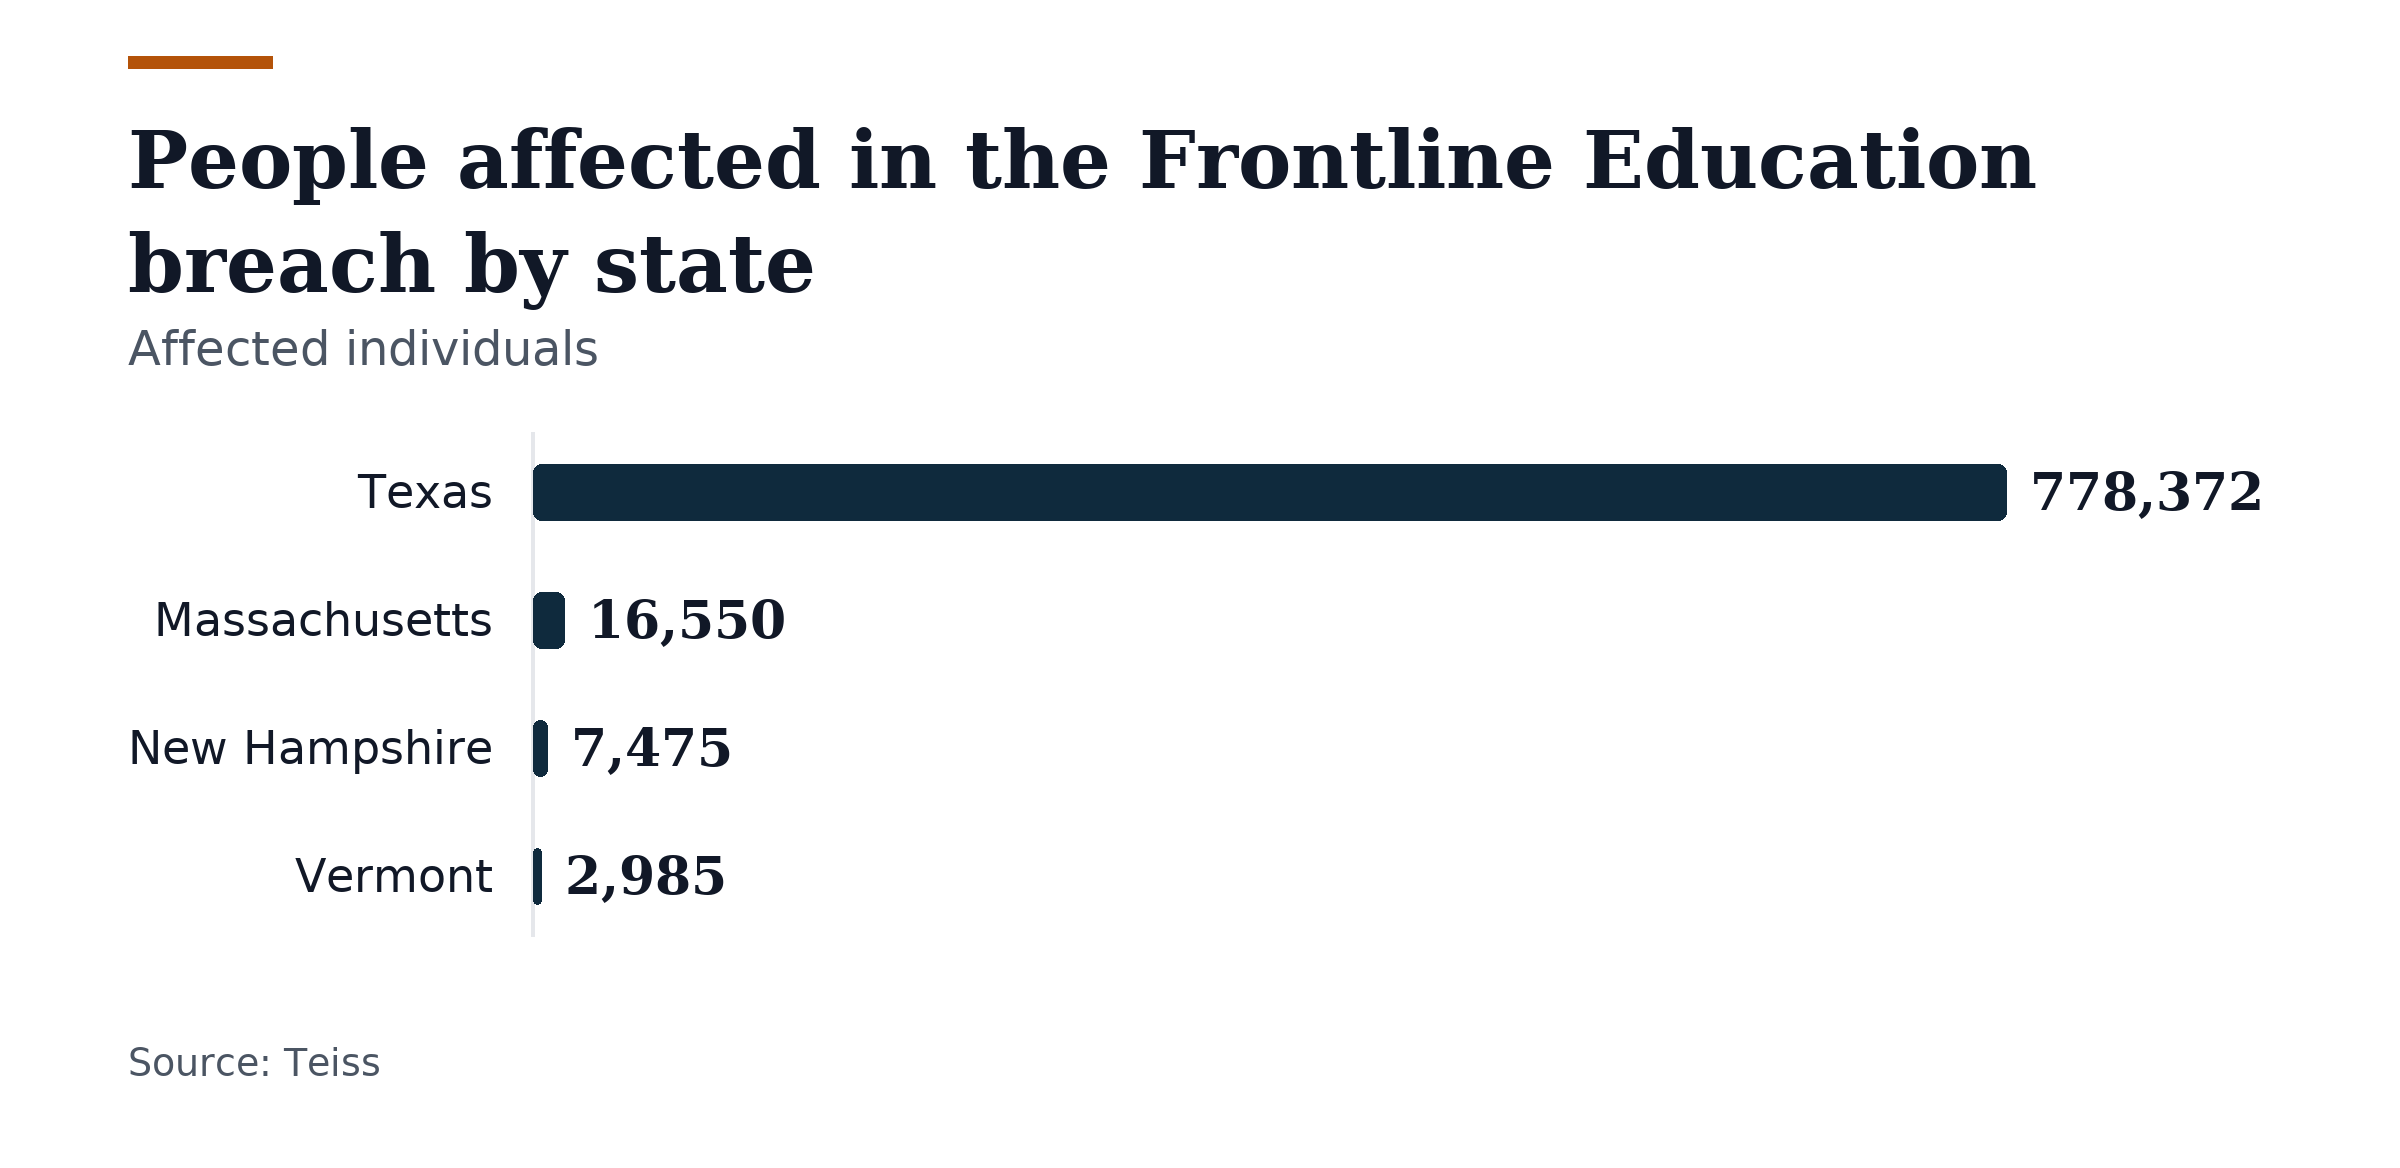
- State regulator filings showed the breach affected 16,550 people in Massachusetts, 7,475 in New Hampshire, 2,985 in Vermont and 778,372 in Texas.
- The reported total across those four states was 805,382 individuals.
- Frontline said the impacted data elements vary by person.
State regulator filings put the affected total at 805,382 people across four states. Frontline Education confirmed that attackers exploited a flaw in software from an outside provider to access sensitive information tied to K-12 school districts in August 2026, and the company’s security team found the flaw on August 14, 2026.
State regulator filings put the affected total at 805,382 people across four states. The counts were 778,372 in Texas, 16,550 in Massachusetts, 7,475 in New Hampshire and 2,985 in Vermont.
The company did not disclose how many school districts rely on the affected products, or how many notification letters it is sending. The company said the affected data elements vary by person. The exposed information includes Social Security numbers, dates of birth, driver’s license numbers, passport numbers, other government ID numbers, Medicaid IDs and student IDs.
For one district, a notification viewed by BleepingComputer showed that every employee had exposed information including Social Security numbers, e-mail addresses and physical addresses. An administrator’s district notice from Frontline put affected employees at 1,210, with Social Security numbers, e-mail addresses and addresses exposed. Frontline has not disclosed when unauthorized access first occurred.
The company has not named the third-party product or vulnerability, has not identified the attacker, and said no established ransomware cartel has publicly claimed responsibility. It also did not disclose who was behind the attack, how much data was compromised, or whether it received a ransom demand. Frontline said it is not aware of any misuse of the exposed data.
Infosecurity Magazine reported that as of October 5, Frontline had not publicly confirmed the breach. A customer published a Frontline notification on Reddit on October 2, showing the breach was discovered almost two months earlier.
Michael Centrella, head of public policy at SecurityScorecard, said districts should learn which records the vulnerable application could reach and whether similar access paths remain elsewhere. “The important security question is what that vulnerable application could reach.” Infosecurity Magazine said the exposed details could support more convincing phishing attacks and identity fraud such as tax scams and new account fraud.
Notices are being sent by email or U.S. mail. Frontline will handle notifications for affected individuals on behalf of districts unless a district opts out by October 16. Districts can opt out through www.frontline-transunion.com or by calling 833-516-8792. The company will not provide notification services or reimburse districts that opt out for their own notice costs.
Frontline offered complimentary credit monitoring services through TransUnion to all affected individuals: two years of free credit monitoring and identity theft protection for affected adults in the United States, and cyber and dark web monitoring where available for minors. The company advised affected individuals to monitor credit reports, account and benefit statements and to report suspicious activity to police and state attorneys general.
Join the discussion