

Key facts
- The company has not identified the third-party product that was exploited.
- No known cybercrime group has taken credit for the incident.
- On August 14, 2026, Frontline's security team found a flaw in a third-party product that allowed unauthorized access to part of its network.
- The company began an investigation with outside cybersecurity experts, contained the breach and notified law enforcement.
Frontline Education told Indiana regulators that an August 2026 breach affected more than 3 million people, and the company set the affected total at 3,085,266 individuals.
Intruders entered part of Frontline’s environment by exploiting a vulnerability in third-party software, and the company’s security team detected the intrusion on August 14, 2026. Frontline said it found a flaw in a third-party product that allowed unauthorized access to part of its network that day.
Frontline’s disclosure listed names, Social Security numbers, birthdates, driver’s license numbers, passport and government ID numbers, Medicaid IDs, and student IDs as possibly exposed. Stolen data came from the Frontline Central and School Health Management products. Infosecurity Magazine reported that the stolen data included Social Security numbers, e-mail addresses and physical home addresses, and the publication said the details could enable convincing phishing attacks and identity fraud such as tax scams and new-account fraud.
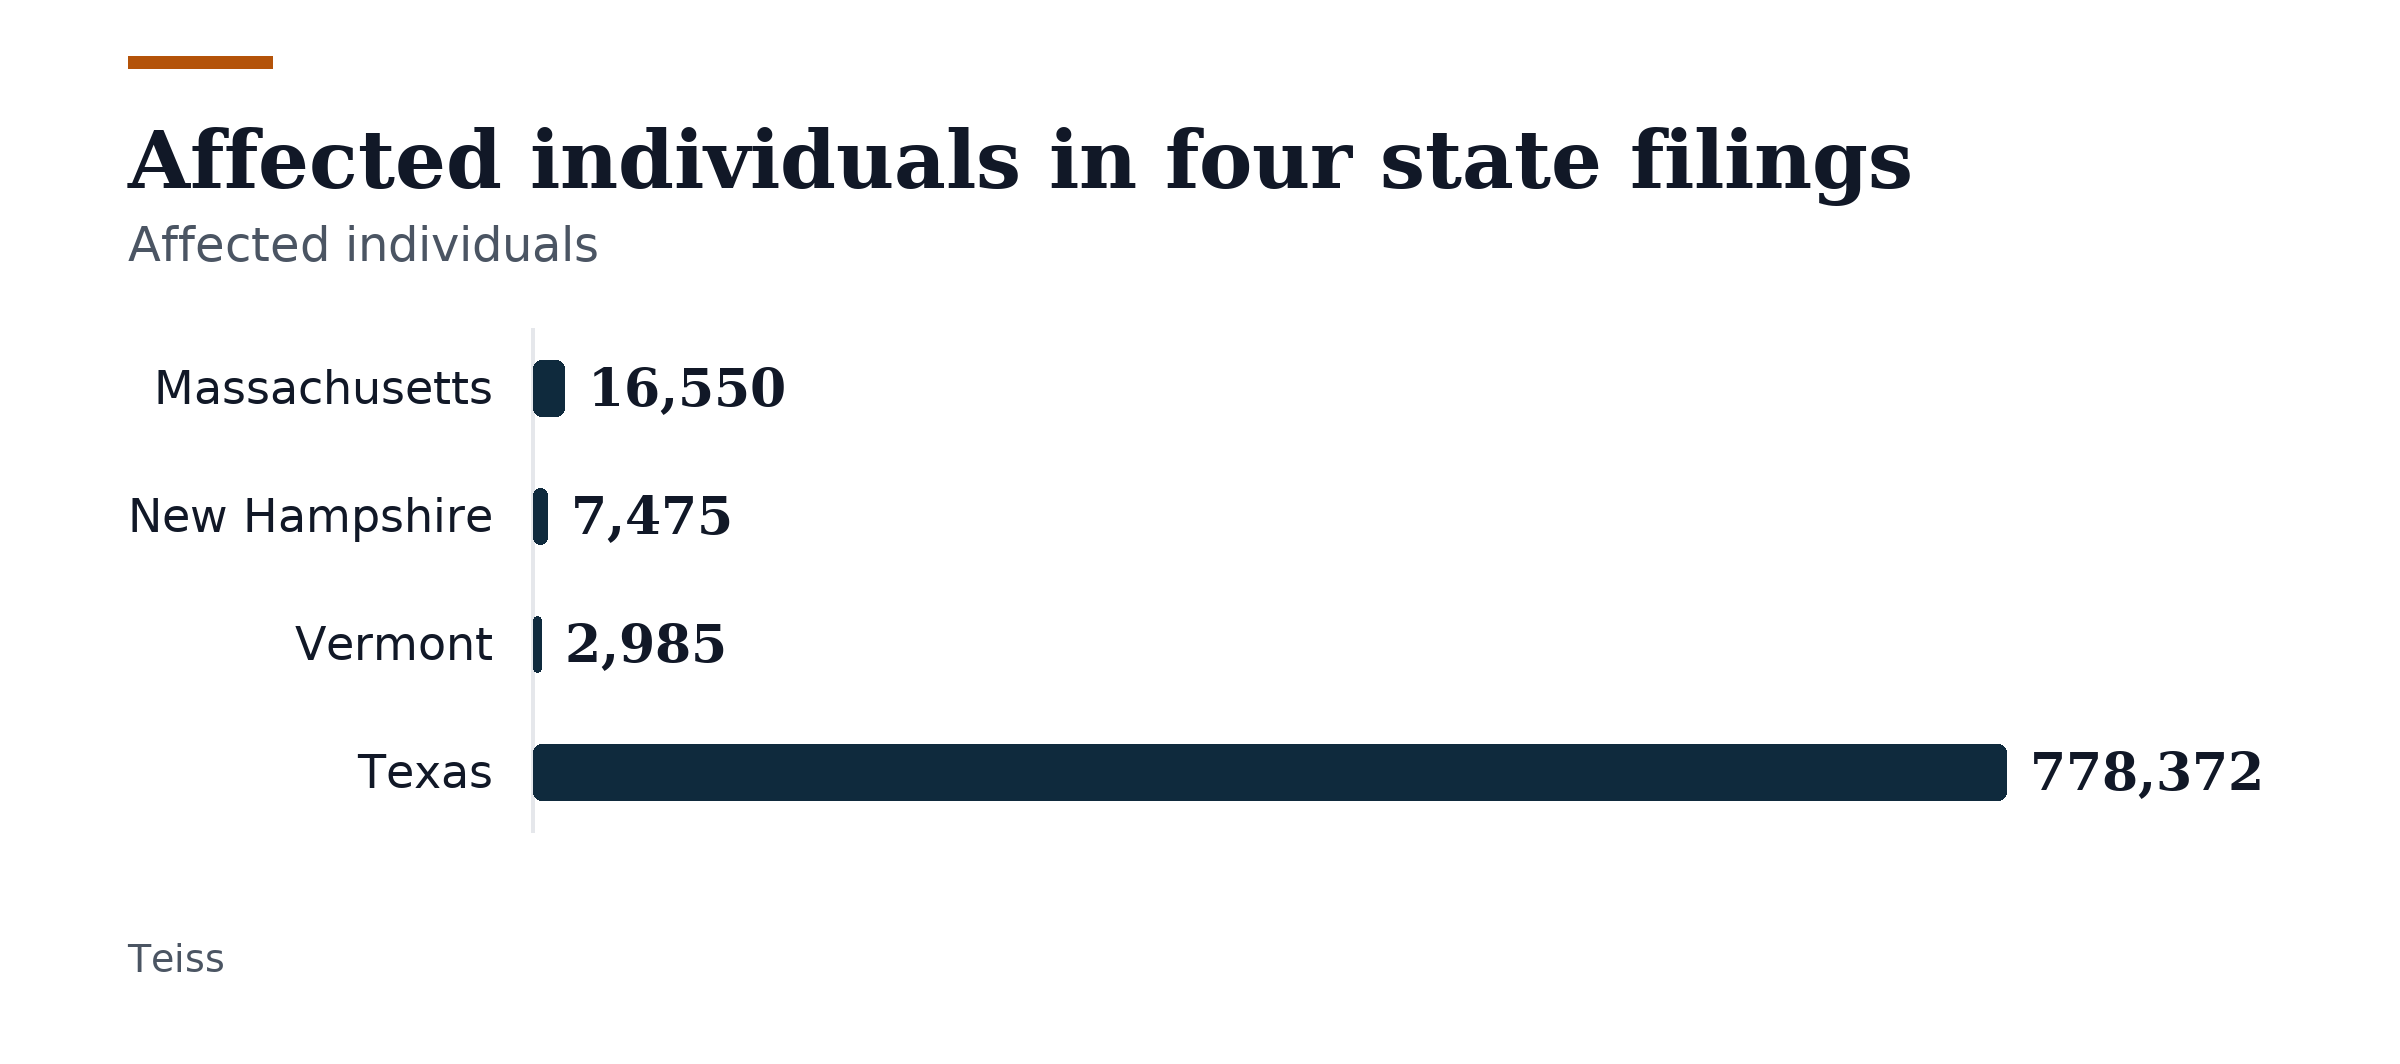
Earlier filings with several other states totaled roughly 1.3 million people, including 16,550 in Massachusetts, 7,475 in New Hampshire, 2,985 in Vermont and 778,372 in Texas. Helena Public Schools said roughly 2,000 current and former employees were caught up, and exposed records covered five years of employee data while student records were not affected. The district learned about the breach from Frontline earlier in October 2026. Frontline said exposed details covered identification including Social Security numbers, birth dates, driver’s license numbers, passport numbers and other identifying details.
For one district, the notice said all staff members were affected and exposed data included Social Security numbers, email addresses and home addresses, while a shared district notice listed 1,210 affected employees with the same exposed details. Posters on the K12SysAdmin subreddit said district officials were receiving similar breach notices, and an administrator reported that a superintendent and business manager got a notice on October 1 from frontline@notifications.cyberscout.com. Additional administrators said they had verified the notices on their own. The notification letter states that intruders gained access by exploiting a flaw in a third-party application.
Infosecurity Magazine reported that a Frontline notice surfaced on Reddit on October 2, 2026, through a customer post, indicating the breach was detected nearly two months prior. The customer-posted notice states that Frontline had no knowledge of any data misuse. No public confirmation of the incident had been issued by Frontline as of October 5, 2026, and the full count of affected districts and employees had not been determined as of that date.
Frontline pledged to email and mail affected individuals and post a public notice on its site and through a press release. Notices to affected individuals are going out by email or U.S. mail through cooperating school districts, and the company will issue individual notices for districts that do not opt out by October 16, 2026.
The opt-out website is www.frontline-transunion.com, and the phone number is 833-516-8792, and opting out means Frontline will not supply notification services or pay for the district’s own notices. Frontline will manage required notices to state attorneys general and cover the costs of individual notifications and identity protection.
Frontline began an investigation with outside cybersecurity experts, contained the breach and notified law enforcement on August 14, 2026. The company says it has alerted districts and affected individuals across the country and strengthened its systems. Frontline is based in Wayne, Pennsylvania, and its software manages hiring, employee records, evaluations, leave, substitutes and district reporting on operations, finances and students.
Frontline has not disclosed who was behind the attack, and no known cybercrime group has taken credit. The company has not said how much data was stolen or whether it received a ransom demand, and it has not identified the third-party product that was exploited or said when the unauthorized entry started. The overall count of affected districts and people had not been determined as of October 2, 2026.
Michael Centrella, head of public policy at SecurityScorecard, said districts need to know what records the vulnerable application could access and which controls limited that access. He also urged districts to check whether comparable pathways remain elsewhere in the company’s systems.
The important security question is what that vulnerable application could reach.
Michael Centrella, head of public policy at SecurityScorecard, Infosecurity Magazine
Adults in the United States affected by the incident receive free credit monitoring and identity theft protection for two years, and the company is providing free TransUnion credit monitoring to everyone affected. Minors who qualify receive free dark web monitoring.
If you're getting sent an invoice and you're not the person who generally deals with invoices, don't open it.
John Thomas, president of Systems Technology Consultants, NonStop Local Montana
Frontline told affected people to monitor credit reports and statements for accounts and benefits, and to alert police and state attorneys general about suspicious activity. John Thomas, president of Systems Technology Consultants, advised people to scrutinize e-mails for strange domains, changed signatures and unexpected invoices.
Join the discussion