Key facts
- CISA added six actively exploited vulnerabilities to its Known Exploited Vulnerabilities Catalog.
- CVE-2026-96652 and CVE-2026-96655 are server-side request forgery vulnerabilities in Plex Media Server added to the catalog.
- CVE-2026-106931 is an OS command injection vulnerability in EG Secure Solutions SiteGuard Server Edition added to the catalog.
- CVE-2026-110936 is an uncontrolled search path element vulnerability in Siemens Software Center added to the catalog.
CISA added six actively exploited vulnerabilities to its Known Exploited Vulnerabilities Catalog on Oct. 20, 2026, including four flaws in Plex Media Server and one each in EG Secure Solutions SiteGuard Server Edition and Siemens Software Center.
The four Plex Media Server flaws, collectively called Plex2Shell as The Hacker News reported Oct. 21, 2026, include two server-side request forgery vulnerabilities tracked as CVE-2026-96652 and CVE-2026-96655, an improper neutralization of encoded URI schemes in a web page flaw tracked as CVE-2026-96654, and an external control of file name or path vulnerability tracked as CVE-2026-96656. Server-side request forgery is a technique that forces a server to make requests to internal or external systems. Improper neutralization of encoded URI schemes means a web application fails to clean web addresses that use encoded characters. External control of file name or path lets an attacker influence file or directory locations.
Security researcher Zach Main discovered and reported the four Plex flaws, which chained could permit unauthenticated remote code execution by a remote attacker. Unauthenticated remote code execution lets an attacker run code on a system without logging in. Plex Media Server version 1.43.3.10861, released Aug. 3, 2026, fixes the four vulnerabilities.
Researcher boredhackerblog reported that threat actors are weaponizing the four Plex flaws to spread cryptocurrency miners and proxy malware tools. The Hacker News reported Oct. 21, 2026, that CVE-2026-96652 carries a CVSS score of 5.3 and CVE-2026-96654 carries a score of 6.9.
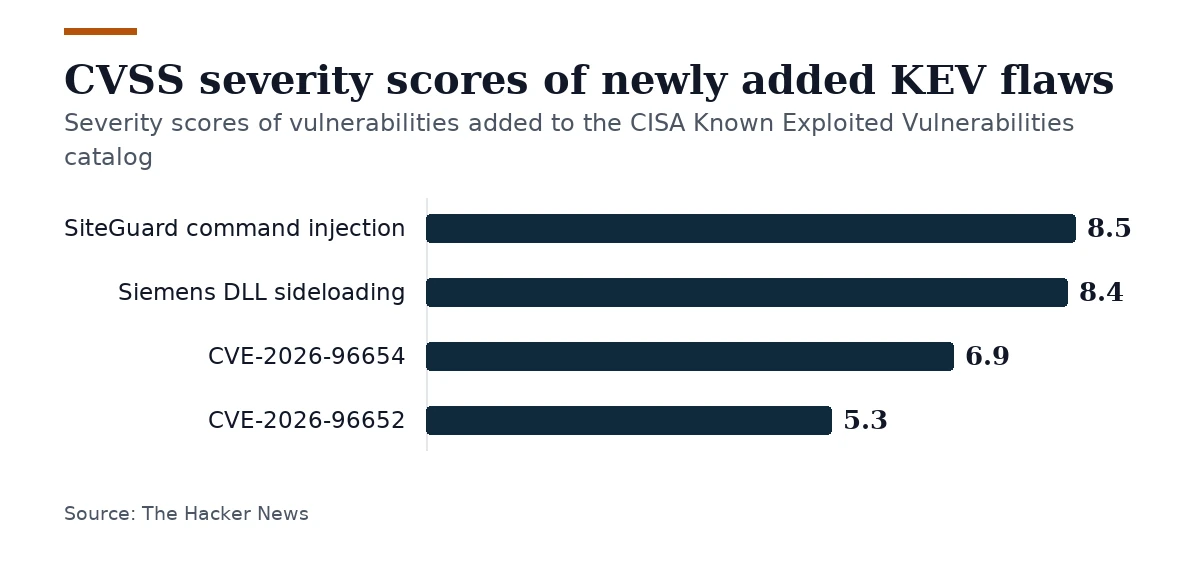
CVE-2026-110936 is an uncontrolled search path element vulnerability in Siemens Software Center. The Hacker News reported Oct. 21, 2026, that the flaw, also described as DLL sideloading, carries a CVSS score of 8.4 and has been abused in ClickFix attacks using the Romulus platform. Uncontrolled search path element lets an attacker place a malicious file where a program will load it, and DLL sideloading places a malicious library where a legitimate application loads it.
CVE-2026-106931 is an OS command injection vulnerability in EG Secure Solutions SiteGuard Server Edition, scored 8.5, and was confirmed exploited by the Japanese company. OS command injection lets an attacker run commands on the underlying system. No further details are available on that exploitation.
CISA describes the six flaws as a common attack route for malicious cyber actors that create major risks for the federal government. Binding Operational Directive 26-04, titled Prioritizing Security Updates Based on Risk, establishes vulnerability management requirements for Federal Civilian Executive Branch agencies. It requires FCEB agencies to put rapid remediation first for high-risk KEV flaws on publicly exposed assets that grant total control after exploitation. The directive also sets expectations for the timing of agency checks for pre-patch compromise by threat actors.
CISA urged FCEB agencies to patch CVE-2026-106931, CVE-2026-96656, and CVE-2026-96654 by Oct. 23, 2026, and the remaining flaws by Nov. 3, 2026. The directive binds only FCEB agencies, but CISA urges all organizations to use risk-based vulnerability management and prioritize KEV fixes.
Private-sector Plex admins and other organizations should prioritize KEV-listed flaws because CISA encourages risk-based vulnerability management and remediation of catalog vulnerabilities. CISA will keep adding vulnerabilities that meet KEV criteria. KEV Nomination Form entries need a CVE ID plus proof of exploitation and clear mitigation steps. “CISA has added six new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation,” CISA said.
Join the discussion