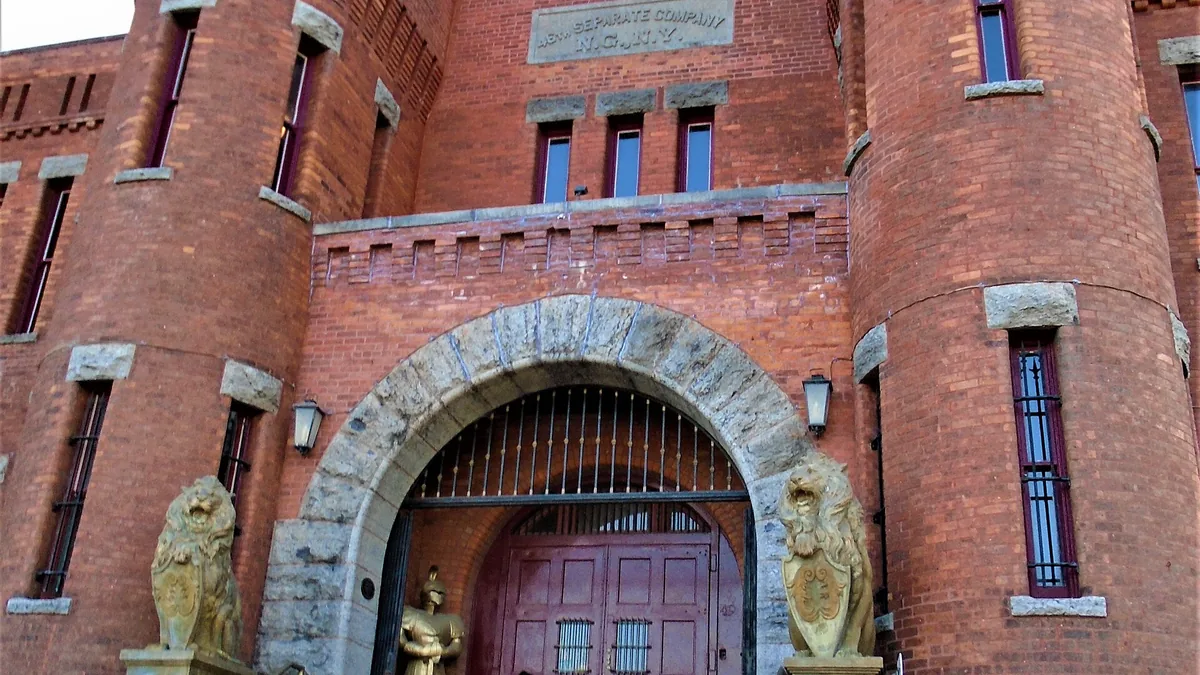
BeyondTrust suspects Armory Castle uses AI to model target products for exploit development
Armory Castle began exploiting BeyondTrust zero-day CVE-2026-102764 on August 29, 2026.
Our coverage: 39 reports since October 8, 2026. Latest: BeyondTrust suspects Armory Castle uses AI to model target products for exploit development, October 18, 2026.
Armory Castle began exploiting BeyondTrust zero-day CVE-2026-102764 on August 29, 2026.
SentinelOne, app.opencve.io, PremierePC Technology Group and TheHackerWire report that the flaw carries a CVSS v3.1 base score of 8.8, rated as high severity.

The flaw carries a CVSS score of 8.8 and is rated Important by Microsoft.
The revised terms, set to take effect October 30, 2026, delete language that let Meta use crawled website content to train its AI products.

Executive Order 14409, signed June 2, 2026, directs agencies to create a classified benchmarking process for AI model cyber capabilities within 60 days.
Lord Ricketts warned that Russian hybrid attacks, which use non‑military tools such as hacking to destabilise a country, are becoming more reckless and dangerous and could result in deaths.
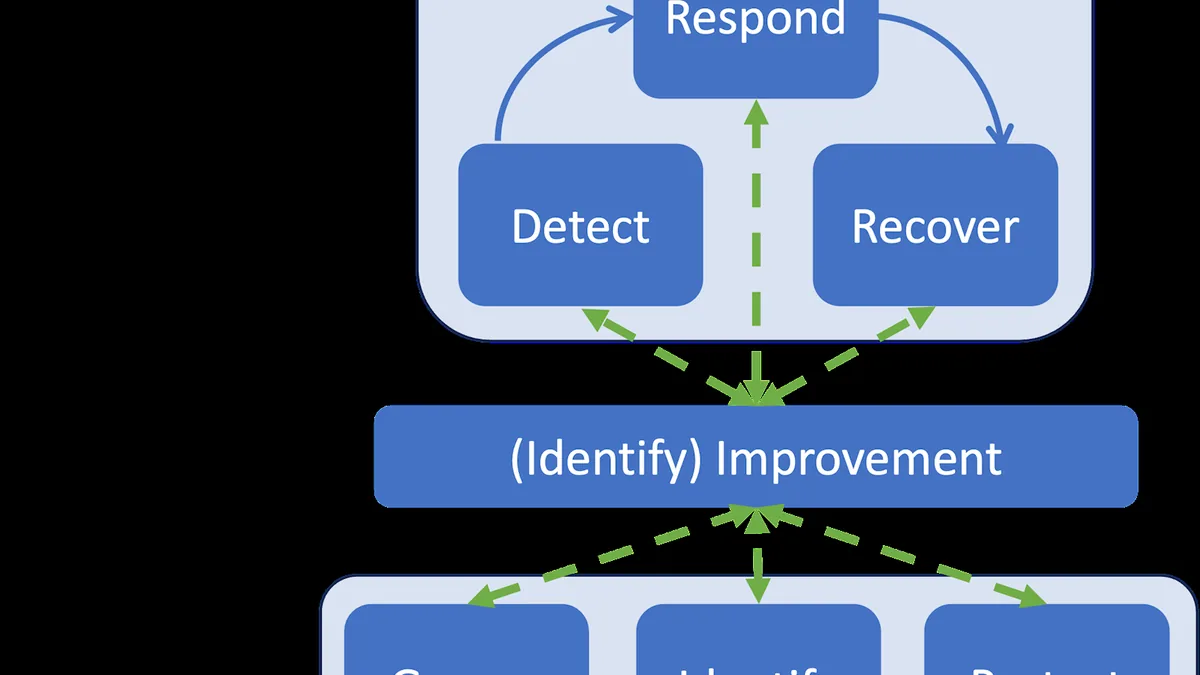
The guideline outlines 10 voluntary core practices for groups that train and assess highly capable super intelligence agents.

The flaws affect EseeCloud App versions ≤4.9.6 and Firmware ≤4.9.86.0, letting attackers gain full control of devices.
CISA reported that CVE-2026-97851 has a CVSS v3.1 base score of 9.1 (Critical) due to missing authorization on a storage status‑change REST endpoint.

The guidance says law enforcement officials should not be at polls unless voting or doing legitimate law enforcement activity.

CISA instructed federal civilian agencies to patch Ivanti Connect Secure vulnerability CVE-2026-104935 by Friday and to address Windows Shell bypass CVE-2026-96951 by Oct. 16, 2026.
The directive follows Volexity’s report of a three‑flaw chain granting root access and notes the flaw’s CVSS 8.6 rating.