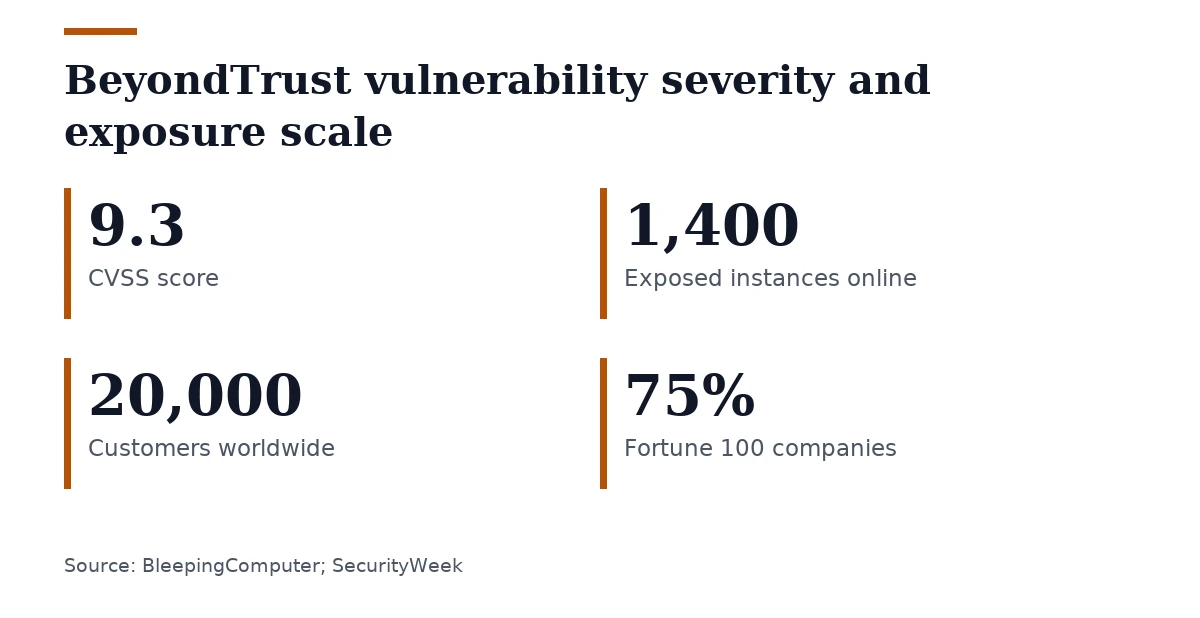
A China-linked espionage group exploited a zero-day vulnerability in BeyondTrust Remote Support appliances starting August 29, 2026. The flaw, tracked as CVE-2026-102764, stems from improper validation of message origins and carries a CVSS score of 9.3 (CVSS scores severity).
The group, identified as Armory Castle—also tracked as UNC5221 and Warp Panda—targeted both BeyondTrust-hosted and self-hosted Remote Support appliances on that date. Mandiant and Google Threat Intelligence Group attributed the activity to the state-sponsored actor, which focuses on long-term intelligence gathering from SaaS providers, tech companies, government entities, legal services, and business-process outsourcers.
BeyondTrust identified the exploitation on September 28, 2026, after a public zero-day against another vendor became known. The company developed a patch by September 30 and shipped it on October 8, with all Remote Support SaaS customers receiving the update by October 9. Self-hosted customers must apply the patch manually unless they have enabled automatic updates.
The vulnerability affects Remote Support versions up to and including 26.2.3. The BT26-05-RS patch includes fixes for versions 24.3.1 through 26.2.3, but customers running older versions must upgrade to a supported release before applying the patch.
After gaining access, Armory Castle deployed the Sawfly webshell and Bareclaw tunneler, both tools used for post-exploitation, to escalate privileges, harvest credentials, and delete logs. The group used compromised administrator credentials to move laterally across networks and exfiltrated sensitive documents, including software inventories, via the BeyondTrust file transfer service.
BeyondTrust provides identity security services to over 20,000 customers worldwide, including government agencies and 75% of Fortune 100 companies. While Shadowserver tracks over 1,400 BeyondTrust Remote Support instances exposed online, it does not show how many remain unpatched or are honeypots.
Join the discussion