Key facts
- Rubrik's Zero Labs reports a median ransomware recovery time of 20 days, measured from recovery start through case closure and full restoration.
- Sixty-eight percent of forensics findings arrived within two days after attack detection.
- Rubrik's report says ransomware attackers increasingly target recovery systems that organizations depend on.
- Of the 16,953 incidents in the report, researchers examined 2,931 cases that described victim extortion methods.
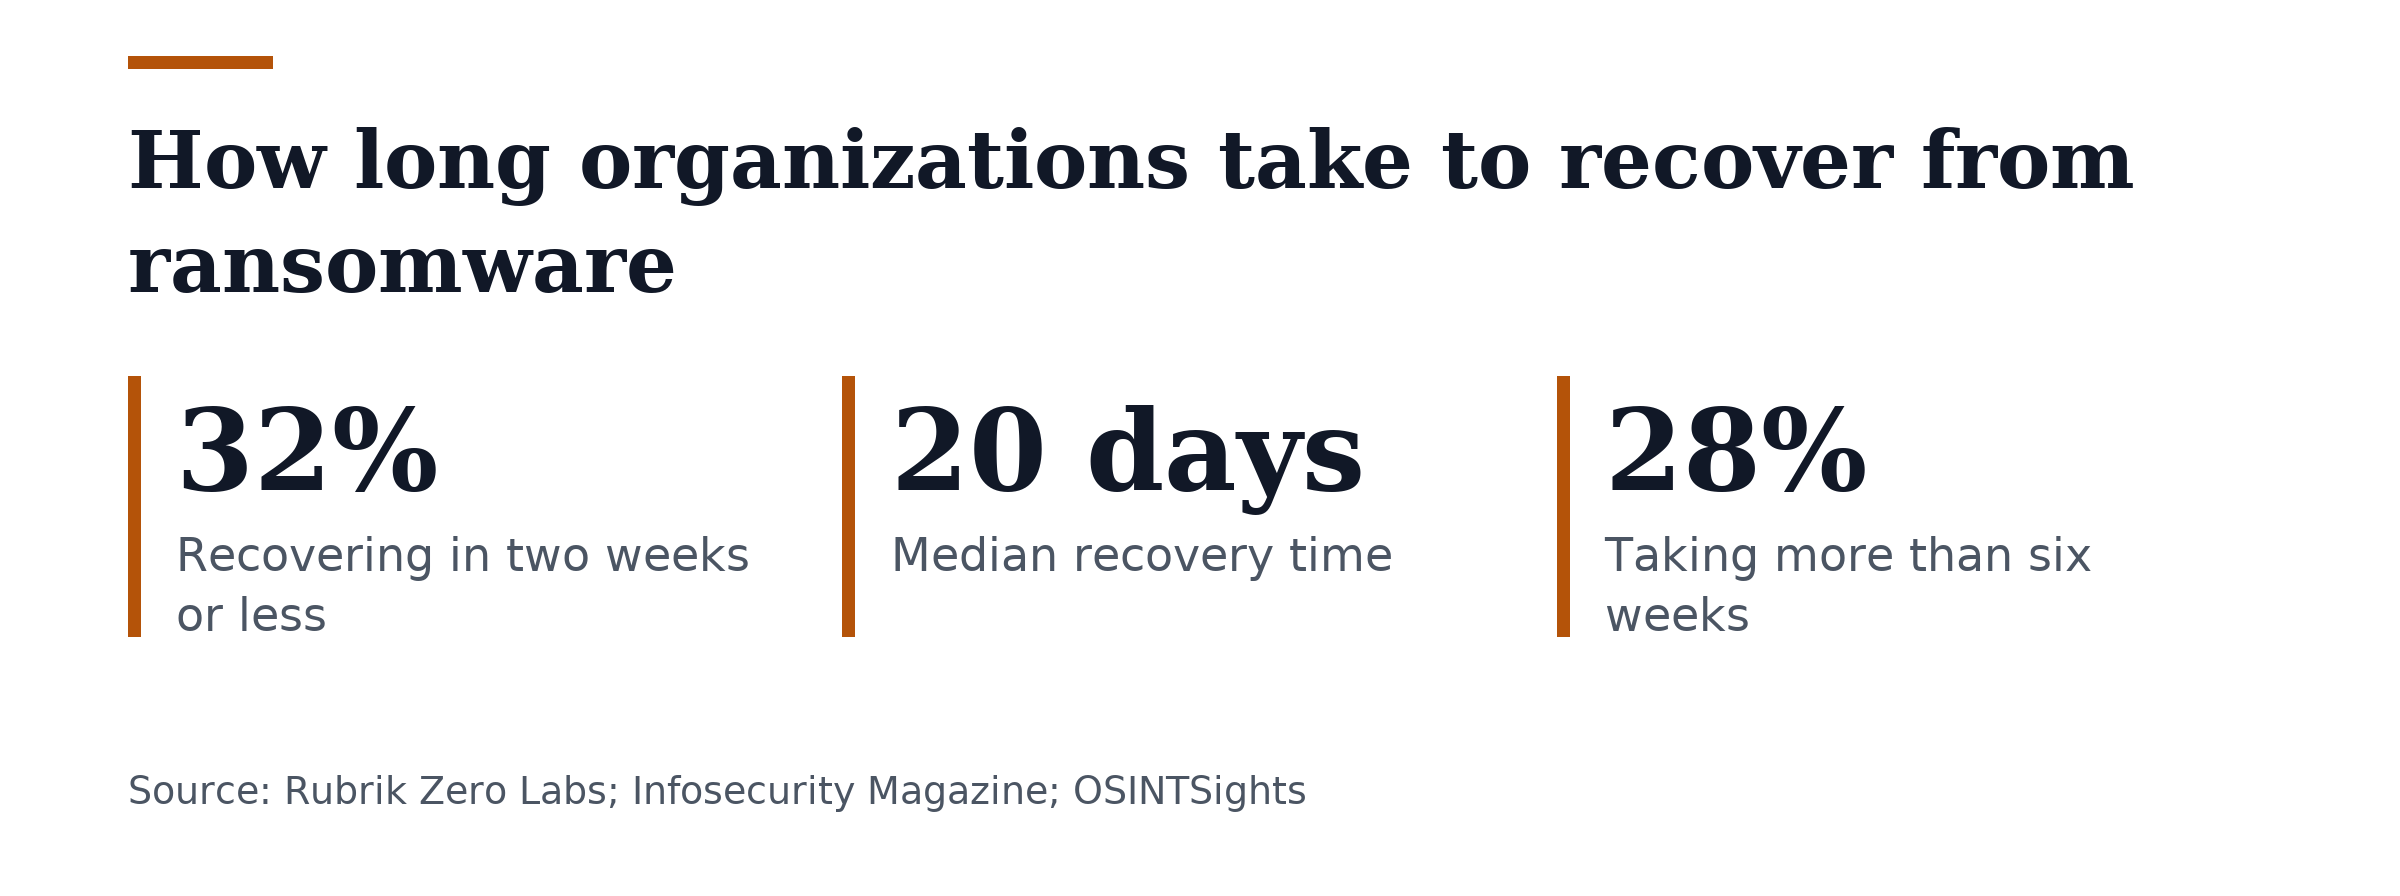
Rubrik’s Zero Labs published a report on November 19, 2026, finding that the median ransomware recovery time was 20 days, measured from recovery start through case closure and full restoration.
Twenty-eight percent of victims required more than six weeks to resume normal operations, forming a long tail beyond the median. Thirty-two percent finished full recovery inside two weeks. Sixty-eight percent of forensics findings arrived within two days after attack detection, with diagnosis fast relative to restoration. The contrast widens the diagnosis-to-recovery gap, and the long tail reflects cases exceeding six weeks.
The report drew on Rubrik’s internal telemetry, real-world recovery cases and 16,953 publicly reported incidents spanning January to October 2026. Researchers examined 2,931 cases that described victim extortion methods. Researchers used the subset to analyze extortion behavior.
Sixty-seven percent of the analyzed extortion cases involved data theft, making data theft the more common extortion lever in the analyzed sample. Forty-five percent explicitly involved encryption, placing encryption in less than half of analyzed extortion cases. Thirteen percent of victims experienced both data theft and encryption. The subset faced both stolen data and encrypted systems.
Rubrik identified 100 active ransomware cartels in 2026. Only eight cartels drove roughly half of all attributed incidents, showing high concentration of activity among some cartels. Qilin, INC Ransom and The Gentlemen together accounted for 30 percent of attributed incidents, the top three cartels among the eight responsible for roughly a third of attributed incidents. Qilin alone was responsible for 15 percent of observed incidents, a single leading cartel in the dataset.
Attackers tried to access backup management consoles in at least 7 percent of ransomware recovery cases reviewed by Rubrik. These were direct attempts to compromise recovery infrastructure observed in real cases.
“Ransomware attackers are increasingly targeting the systems organizations rely on to recover,” Rubrik’s report says. The report also warns that recovery platforms are no longer safe from adversary activity.
OSINTSights states that backups do not guarantee quick recovery when adversaries operate inside backup environments. The outlet frames this as a warning that backup environments are not immune during ransomware incidents. The outlet says security teams must monitor backup environments closely and that planning should cover multi-week recovery timelines.
Join the discussion