Key facts
- Roman Khlynovskiy, a 43-year-old Kazakh national, was extradited from Italy to the United States to face criminal charges.
- Prosecutors allege Khlynovskiy was part of the 8-Digits Team, a group linked to the INC and Lynx ransomware operations.
- The indictment charges Khlynovskiy with a computer fraud conspiracy and an identity theft conspiracy.
- He also faces charges of wire fraud conspiracy, computer-based extortion, and money laundering conspiracy.
Roman Khlynovskiy, a 43-year-old Kazakh national, was arrested in Italy in July 2025 during a family vacation in Rimini, according to BleepingComputer, and was extradited from Italy to the United States. He made his initial appearance in federal court in Knoxville, Tennessee, on Nov. 16, 2026, to face criminal charges alleging ransomware attacks against U.S. hospitals, schools and healthcare entities.
The Justice Department’s indictment charges Khlynovskiy with computer fraud conspiracy and identity theft conspiracy. It also charges him with wire fraud conspiracy, computer-based extortion and money laundering conspiracy. A fifth charge accuses Khlynovskiy of threatening to distribute intimate images without consent under the TAKE IT DOWN Act. A conviction could put him in prison for up to 27 years.
The indictment is only an allegation, and Khlynovskiy is innocent unless proven guilty beyond a reasonable doubt.
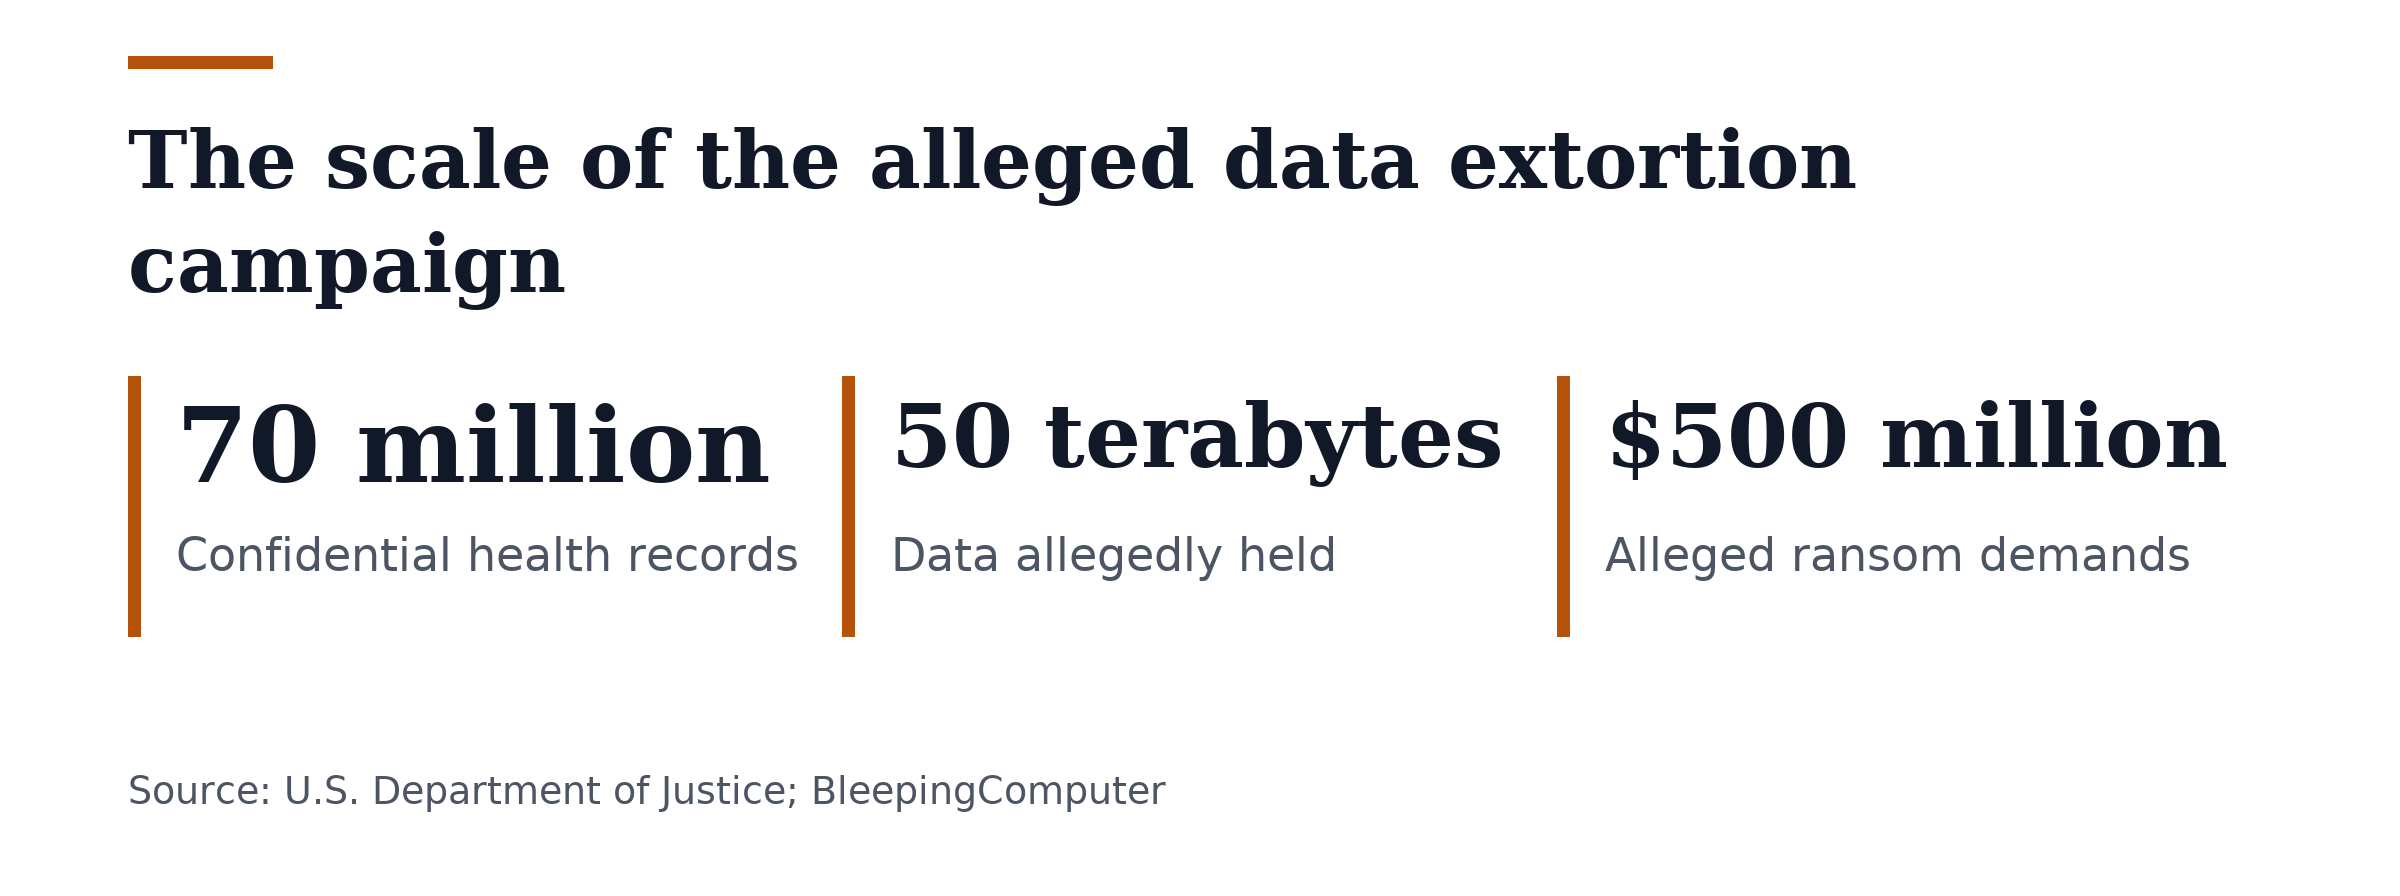
Prosecutors allege the conspirators claimed to hold more than 70 million confidential health records and over 50 terabytes of data. The alleged extortion campaign produced more than $500 million in ransom demands. The Department of Justice said, “The conspirators boasted that they possessed over 50 terabytes of data consisting of more than 70 million confidential health records.”
The conspiracy targeted victims in at least six U.S. states, including both schools and hospitals. Prosecutors allege Khlynovskiy was part of the 8-Digits Team, a ransomware cartel linked to the INC and Lynx ransomware operations.
INC Ransom began as a ransomware-as-a-service cartel in July 2023, according to BleepingComputer, and its leak site lists more than 1,000 victims. The cartel targets education, healthcare, government and industrial organizations.
Lynx ransomware appeared in July 2024 and is considered a rebranding of the INC ransomware operation instead of a new group. Its dark web leak site now lists more than 400 victims. The encryptor likely uses INC Ransom source code as its foundation, and the code was allegedly listed for $300,000 on the Exploit and XSS forums in May 2024. A string analysis by BleepingComputer in August 2024 showed that Lynx and recent INC encryptors were largely identical.
Investigators from Ukraine’s State Bureau of Investigation and Prosecutor General’s Office, along with Lithuanian authorities, gave substantial assistance. Officials from the Justice Department’s Office of International Affairs coordinated with Italy to secure Khlynovskiy’s arrest and extradition.
The FBI is investigating the case. FBI Director Kash Patel said the 8-Digits Team repeatedly targeted hospitals and schools and threatened to release highly sensitive information, stating that the group “repeatedly targeted hospitals and schools, extorting victims and threatening to release highly sensitive information.” Patel pointed to 84 Foreign Transfers of Custody in 21 months, a 71% increase, and to 157 extraditions, up 121%, in the FBI’s effort to return fugitives.
Assistant Attorney General A. Tysen Duva characterized the case as one of the biggest healthcare data security breaches in decades. Duva said the conspirators took large amounts of sensitive patient data and sought profit by threatening vulnerable members of society. The Justice Department quoted Duva as saying, “The defendant is charged with participating in one of the largest healthcare data breaches in decades.”
Prosecutors Thomas Dougherty and Bryce Rosenbower from the Criminal Division’s Computer Crime and Intellectual Property Section are handling the case. Assistant U.S. Attorney Jeremy Dykes for the Eastern District of Tennessee is also prosecuting the case.
Since 2020, the Computer Crime and Intellectual Property Section has won convictions for more than 220 cyber and intellectual property criminals. The section has also secured court orders requiring the return of more than $500 million to victims.
The TAKE IT DOWN Act became law in May 2025, and it makes publishing intimate images without consent a crime. Prosecutors say they are using the act in this ransomware case because threats to release intimate material act as leverage.
Join the discussion