Key facts
- Island researchers disclosed a human-operated phishing platform that poses as advertising products for AI chatbots: Gemini, Claude, ChatGPT, Perplexity, Meta Muse and Manus.
- The displayed address inside a BitB window is part of the page's artwork, so it cannot show where the form sends data. Island advises checking the real browser's outermost address bar.
- The platform fingerprints the victim's device and keeps every password attempt, up to three per visitor. A human operator then attempts a real login and chooses which MFA challenge the victim sees next.
- Operators can request SMS or authenticator codes, show Google approval, QR or number-matching prompts, or show Okta push prompts. They can also reject codes, hold victims on a waiting screen, or end the flow.
Island researchers disclosed a human-operated phishing platform on Oct. 6, 2026, that poses as advertising products from Gemini, Claude, ChatGPT, Perplexity, Meta Muse and Manus. According to The Hacker News, the fake products are built to capture passwords and multifactor authentication (MFA) codes, the one-time codes or approvals that normally protect a login. The people in the crosshairs are ad agency staff and the clients whose accounts they run.
BleepingComputer reports that the Telegram channel the operators use to control the pages received hundreds of victim submissions. That figure does not equal the number of compromised accounts, and BleepingComputer reports that no verified total of takeovers or losses has been published. No victim organization has been named as confirming a takeover in the reporting, so what follows is the researchers’ description of the platform.
What an agency stands to lose
The Hacker News reports that stolen ad accounts can be used to run fraudulent ads or be resold, and that attackers often add their own administrators and downgrade the owner. For an agency, that means losing control of a client’s campaigns while the client’s budget may pay for someone else’s ads.
Getting an account back is slow. The Hacker News reports recovery can take weeks or months, which leaves live campaigns stalled and clients waiting on answers. BleepingComputer reports the intended targets are agency staff, media buyers and manager-account administrators, the people who hold access to many accounts at once.
How the lookalike login works
The Hacker News reports the fake products pitch campaign tuning, spend audits and links to business accounts. Each is built around a Connect button. Clicking it opens a window drawn inside the real browser, a technique called browser-in-the-browser, or BitB.
The pretend address bar in that window shows a trusted site, such as a Google sign-in domain or a company’s Okta login page, per The Hacker News. Meanwhile, the real browser stays on the attacker’s domain. Cyber Security News reports that the address shown inside the window is part of the page’s artwork, so it cannot show where the form sends data.
BitB is not new. BleepingComputer reports that researcher mr. dox devised it in March 2022 and that it has been used against targets such as Steam accounts. The fake window is an iframe, a web page embedded inside another page.
The kit also dresses itself for the device in front of it. Cyber Security News reports it adjusts for Windows, macOS, iOS and Android, including dark mode and mobile browser styling. BleepingComputer says it rebuilds provider sign-in screens locally and collects credentials through its own APIs instead of proxying the real sites, so its traffic looks like an AI product talking to an unrelated backend.
A live operator handles the MFA step
This is what separates the platform from a static fake form. The Hacker News reports it fingerprints the victim’s device and keeps every password attempt, up to three per visitor. A human operator then attempts a real login and chooses which MFA challenge the victim sees next.
BleepingComputer reports operators can request SMS or authenticator codes, show Google approval, QR or number-matching prompts, or display Okta push prompts. They can also reject a code, hold the victim on a waiting screen, or end the session. The Hacker News adds that commands reach the page through two channels, operator-command and telegram-command, which feed the same parser.
How victims arrive, and why the timing matters
Island assesses that victims arrive through fake invitation emails, The Hacker News reports. One documented case was a Gemini Ads beta invitation that reached a paid-media manager in late August 2026. The report says other delivery routes may exist.
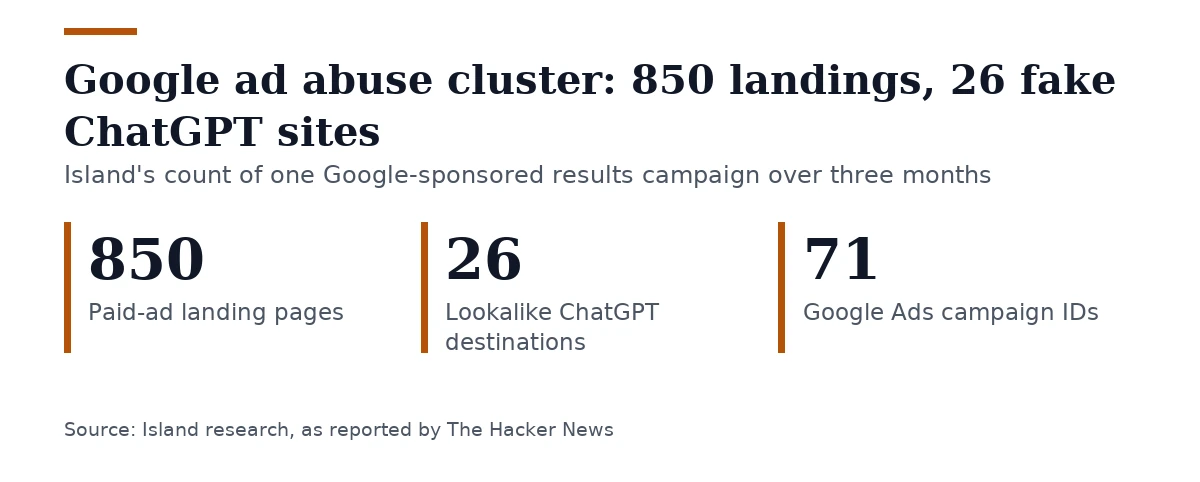
The lures track the news cycle. Cyber Security News reports that the museads.ai lure appeared on Sept. 16, 2026, about a week or eight days after Meta announced its Muse agent on Sept. 8, 2026.
A new AI product from a big vendor gives an agency employee a plausible reason to expect an invitation to something.
A wider platform
BleepingComputer reports that the AI ad pages belong to a broader platform that also runs Google Ads refund and payment pages and recruitment lures using the names Tesla, Louis Vuitton, Nike and Adecco. All share a Next.js and Socket.IO stack. Socket.IO is a library for real-time messaging between server and browser, which is what lets an operator steer a victim’s screen.
BleepingComputer also reports that the operators left older source code in misconfigured public GitHub repositories, which let researchers trace the activity back to March. Archives show 73 scans of 25-page domains from May 27 to June 20, 2026, the outlet says.
Telling a real vendor login from a fake
Two checks come from the reporting. BleepingComputer reports that a BitB window is an iframe, so unlike a genuine OAuth popup it cannot be dragged outside the browser window or resized. OAuth is the standard that lets one service sign in through another.
Island advises checking the real browser’s outermost address bar, Cyber Security News reports. Because the address inside a BitB window is only drawn artwork, the outer bar is the one that reflects the page actually loaded.
Defenses named in the reporting
Cyber Security News lists phishing-resistant authentication such as passkeys or hardware-backed methods, review of changes to ad-account control, scrutiny of AI integrations, and confirming unexpected beta programs through official vendor sites. The Hacker News also points to phishing-resistant authentication.
After possible exposure, Cyber Security News says administrators should go through each client account they can reach for managers they do not recognize, altered recovery details, and campaigns or spend nobody approved.
Why it matters
The scheme relies on a fake login window and an operator who can answer whatever MFA prompt appears, according to The Hacker News and BleepingComputer. Because the operator picks the challenge, a code typed into the page is not protected by the fact that the account has MFA turned on.
The reach of the wider platform, from AI ad tools to refund pages and recruitment lures, suggests the operators reuse one kit across themes. No verified count of takeovers or losses exists yet, so the scale remains open.
Join the discussion