
Key facts
- The flaw was actively exploited in extremely sophisticated targeted attacks against specific individuals on iOS versions before iOS 27.
- Apple has backported patches for CoreGraphics zero-day CVE-2026-86950 to older iPhones and iPads not included in last month's patches.
- Newly covered iPhones: iPhone XS, iPhone XS Max, and iPhone XR.
- The September fixes covered iPhone 11 and later.
Apple has backported patches for CoreGraphics zero-day CVE-2026-86950 to older iPhones and iPads not included in the fixes released on September 28, 2026.
Meta Product Security discovered the out-of-bounds write weakness tracked as CVE-2026-86950 in CoreGraphics. Attackers actively exploited the flaw in extremely sophisticated targeted attacks against specific individuals on iOS versions before iOS 27. TidBITS said on Sept. 28, 2026, that attackers are probably exploiting the CoreGraphics flaw in spyware like Pegasus.
Apple says CoreGraphics handles two-dimensional vector graphics, text drawing, and image rendering on iOS, iPadOS, macOS, watchOS, and tvOS. The company says processing a maliciously crafted file may result in arbitrary code execution through the flaw. Out-of-bounds write flaws can crash programs, corrupt data, or give attackers remote code execution.
Digital Trends said on Sept. 30, 2026 that it is unknown how attackers delivered the file or whether any victim interaction was required. The outlet also said public evidence does not connect the attacks to WhatsApp, Instagram, or another Meta service.
The newly covered iPhones are the iPhone XS, iPhone XS Max, and iPhone XR. The fixes released on September 28, 2026 covered iPhone 11 and later.
The backport also reaches older iPad hardware: the iPad 7th generation, iPad Air starting with the 4th generation, iPad starting with the 9th generation, and iPad mini starting with the 6th generation. Last month’s updates reached newer iPad Pro hardware, including the 12.9-inch model from the 3rd generation onward and the 11-inch model from the 1st generation onward, plus the iPad Air from the 3rd generation onward, the iPad from the 8th generation onward, and the iPad mini from the 5th generation onward.
Apple says affected Macs include those running macOS Sequoia 15.8.1 and Tahoe 26.7.1. Apple says Lockdown Mode is designed for people facing highly targeted threats. On September 28, 2026, Apple shipped those fixes as iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1.
The backport extends CoreGraphics zero-day protection to older supported iPhone and iPad hardware that missed the September 28, 2026 fixes. Apple says CVE-2026-86950 was found by Meta Product Security and was used in extremely sophisticated targeted attacks on iOS versions before iOS 27. A maliciously crafted file may lead to arbitrary code execution through the image-processing framework.
Digital Trends said on Sept. 30, 2026, that the delivery method and whether victims needed to interact remain unknown. Apple urges users to install the backported updates to block potential attacks. The backported updates are available for the newly covered iPhone and iPad models.
Apple said on Oct. 27, 2026 that it knows of a report that attackers exploited the issue in extremely sophisticated attacks against specific individuals. “Apple is aware of a report that this issue may have been exploited in an extremely sophisticated attack against specific targeted individuals” — Apple.
On Sept. 30, 2026, Cobalt CISO Andrew Obadiaru urged security leaders to review mobile update enforcement, protections for high-risk individuals, and incident response plans. “I’d encourage teams to use this as a prompt to review three things” — Andrew Obadiaru, Cobalt CISO.
This year Apple fixed two zero-days exploited in attacks; CVE-2026-20700 in dyld was the other, patched in February 2026. In 2026, Apple also fixed a Beats Studio Buds flaw tracked as CVE-2025-20701 that lets attackers in Bluetooth range spy on conversations. Apple patched older iPhones and iPads for four flaws tied to cyberespionage and crypto-theft attacks that used the Coruna exploit kit.
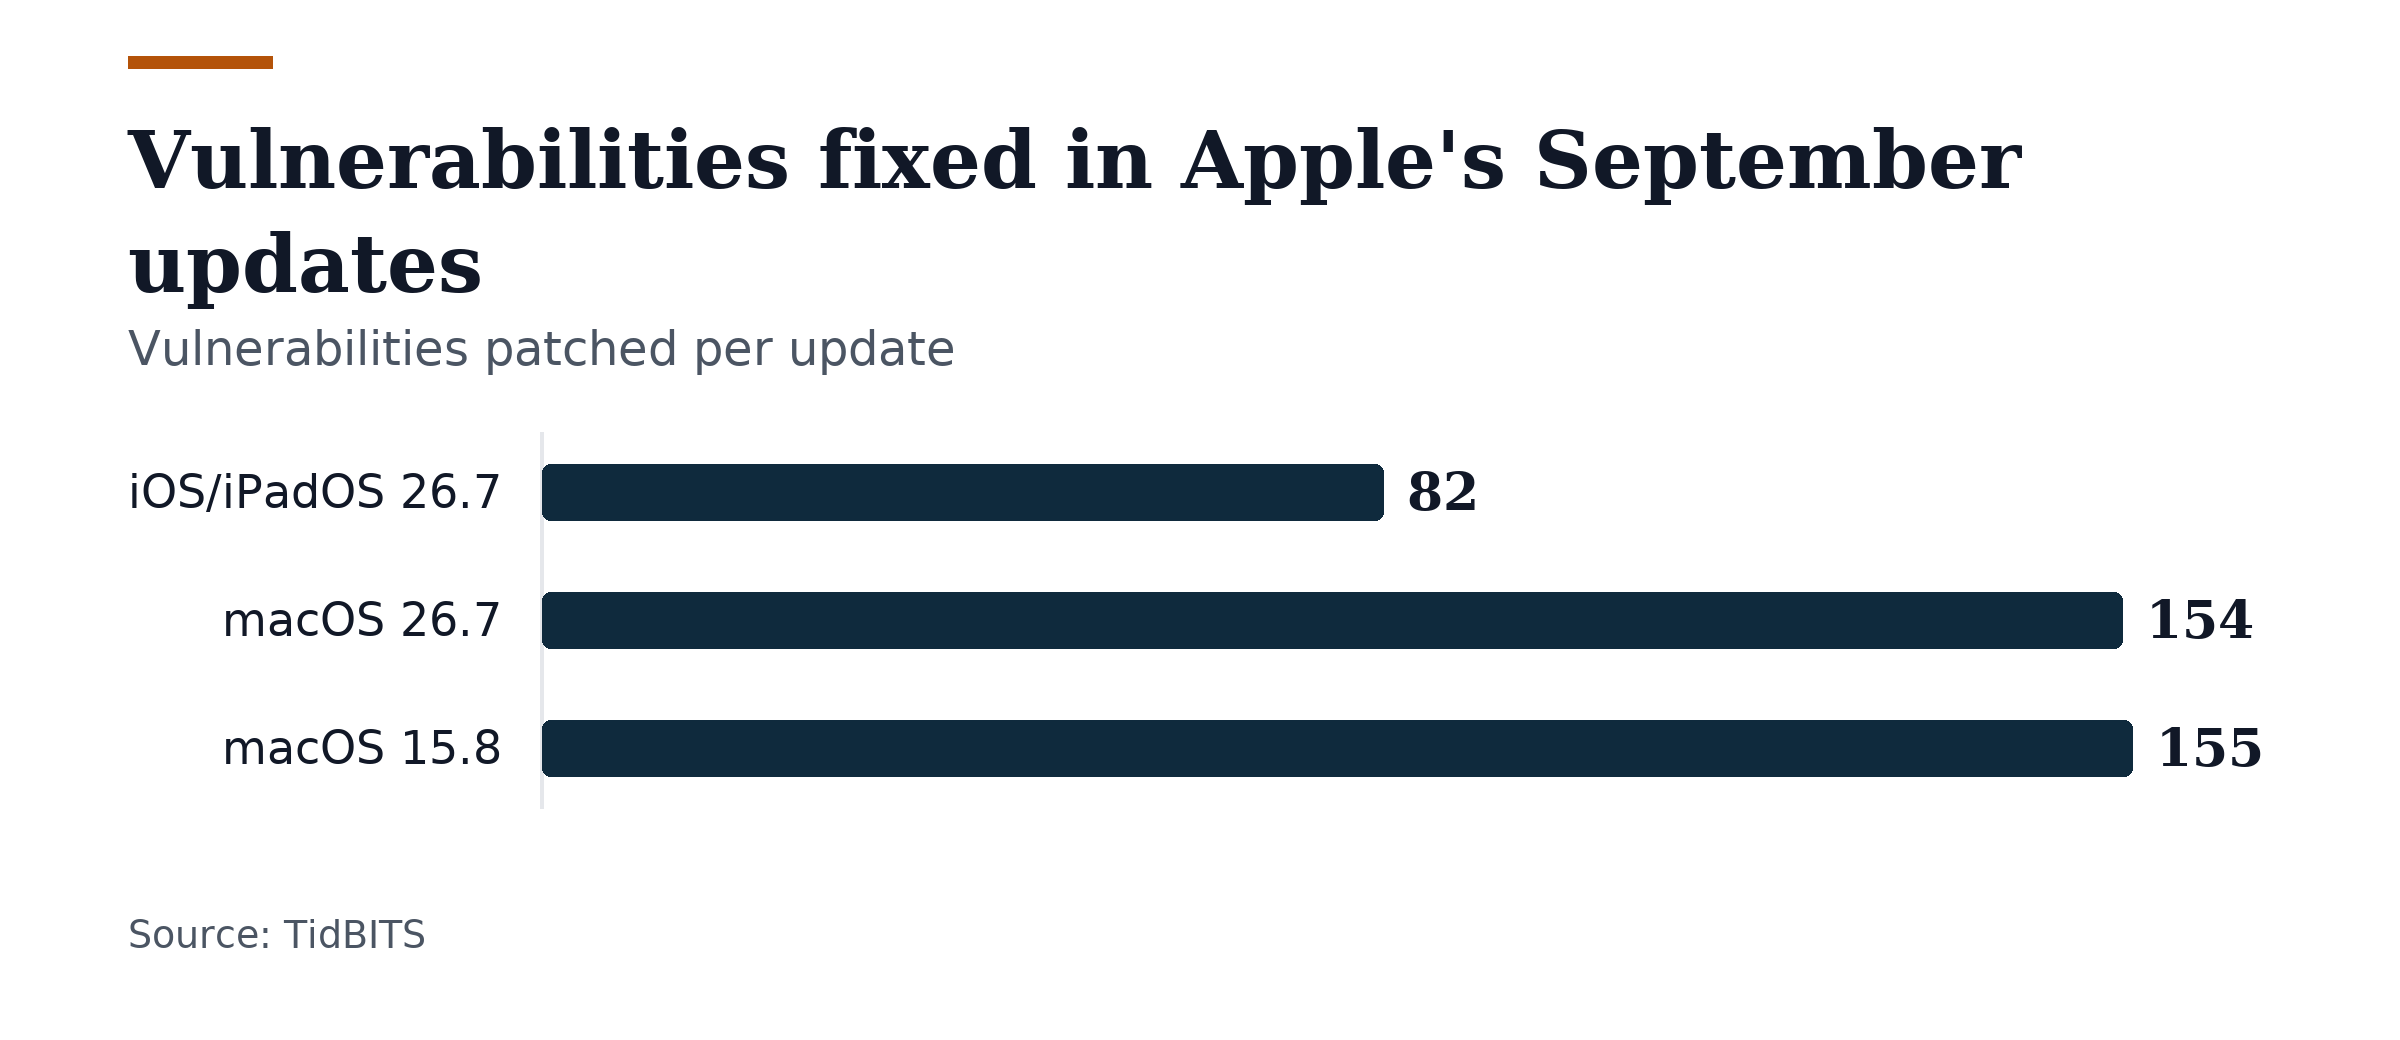
The September 28, 2026 updates fixed 82 vulnerabilities in iOS and iPadOS 26.7, 154 in macOS 26.7, and 155 in macOS 15.8. In February 2025, Citizen Lab found CVE-2025-24200, which Apple said was exploited in an extremely sophisticated attack against a specific targeted individual. Apple also patched CVE-2026-86869, a critical zero-click iMessage vulnerability, in September 2026.
Join the discussion