
Key facts
- Sony Network Communications disclosed that attackers accessed the So-net member database and took personal information, including email passwords for 54,401 users, from more than 2.58 million customers.
- The company halted the affected server and severed communications from the source that gained unauthorized access.
- Japan's Personal Information Protection Commission received a report about the incident from the company.
- The affected So-net membership records total 2,141,986, comprising 1,869,771 current members and 272,215 former members whose service ended in March 2026 or later.
On Oct. 27, Sony Network Communications said intruders entered the So-net member database and removed personal data, including email passwords for 54,401 users, affecting more than 2.58 million customers. Sony Network Communications, part of Sony Group, runs consumer internet services such as So-net and NURO in Japan alongside corporate technology services. The intrusion occurred on Oct. 19, and Sony Network Communications confirmed it on Oct. 23.
On Oct. 23, the company shut down the affected server and cut off communications from the source that had gained unauthorized access, acting immediately after confirmation. An investigation finished the following day, on Oct. 24, confirmed that personal data had leaked and identified the information categories and record counts. Sony Network Communications said the investigation into the intrusion method and full impact remains ongoing as of Oct. 27.
So-net membership records affected by the breach total 2,141,986, made up of 1,869,771 current members and 272,215 former members whose service ended in March 2026 or later. A separate set of 443,495 plala (S Course) records covers 422,365 current members along with 21,130 former members. Customers who canceled by the end of February 2026 are not included among those affected.
Personal details taken from membership records included user IDs, birth dates, gender, internet connection IDs, names, phone numbers and e-mail addresses. The company said no passwords leaked for these membership records, setting them apart from the compromised e-mail credentials. The 54,401 affected e-mail addresses belong to current or former So-net members already included in the membership totals rather than representing additional customers.
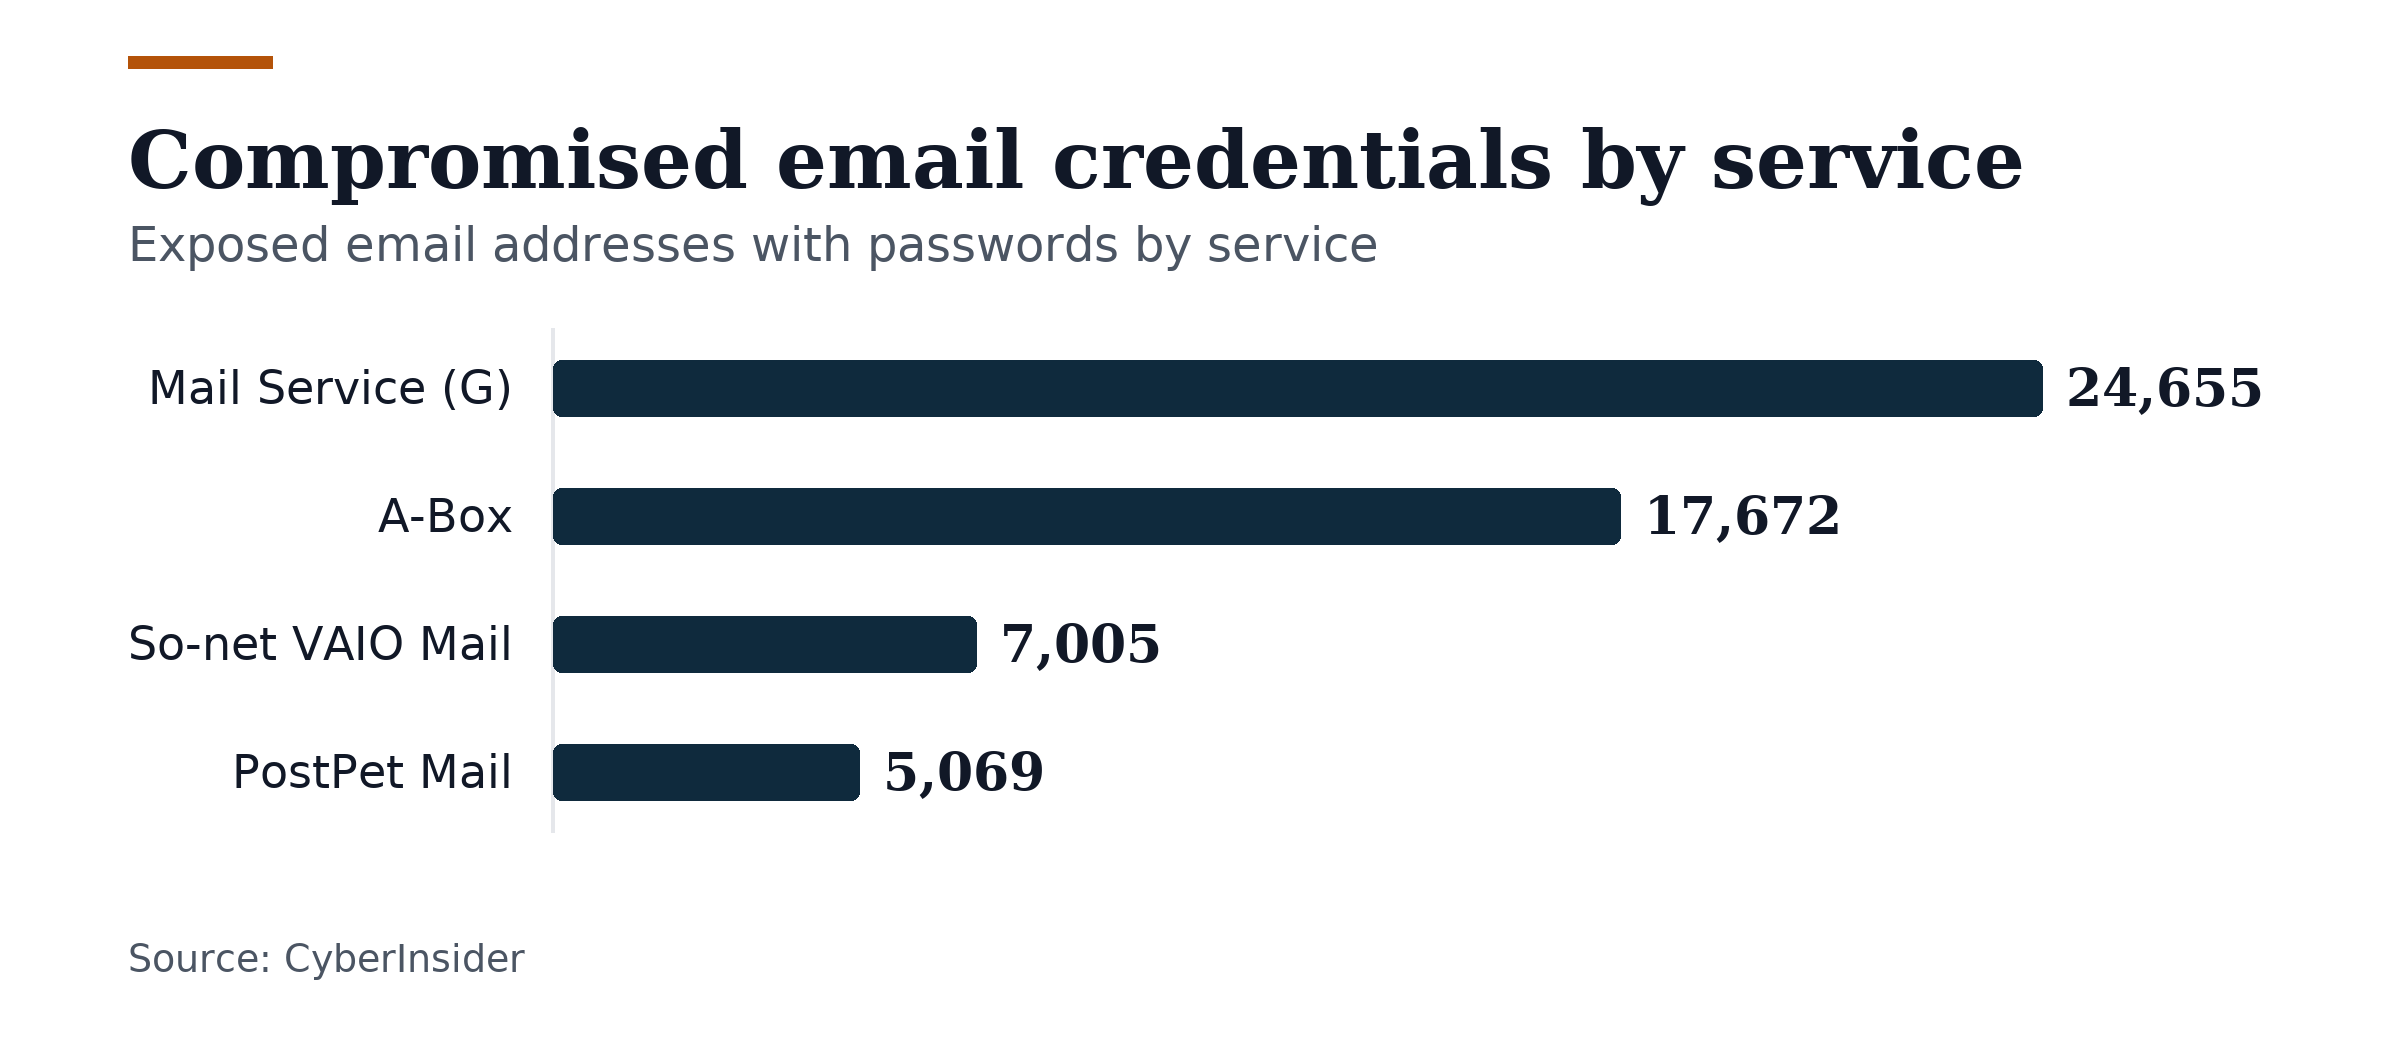
Intruders took both email addresses and passwords for 54,401 addresses spread across four email services offered to So-net members. The count by service is 24,655 for the free Mail Service (G), with 17,672 on A-Box additional mailboxes, 7,005 on So-net VAIO Mail and 5,069 on PostPet Mail Account Service. Sony Network Communications has not revealed the storage method for the compromised email passwords. Seven password-reset notices sent to members had their data exposed on Oct. 27, and those passwords have been reset.
The leak also includes 16 bank account records, and those records contain branch and bank names, account types, numbers and the names of the people who hold the accounts. Sony Network Communications said it does not hold bank account PINs. No plala (S Course) customers are affected by the bank account portion of the leak. No credit card information appeared in any exposed data category, the company said.
Sony Network Communications described the cause of the breach on Oct. 27 as unauthorized access by a third party. The company filed a report about the incident with Japan‘s Personal Information Protection Commission on Oct. 27. Sony Network Communications said it takes the incident seriously and promised to keep examining the cause while reviewing security measures and its information management system. On Oct. 27, Sony Network Communications said no secondary damage from the incident had been confirmed.
We have confirmed an information leak caused by unauthorized access to the member database
Sony Network Communications, Help Net Security
Sony Network Communications warned that leaked information could enable future suspicious communications. Customers should not respond to suspicious e-mails, text messages or phone calls, and they should not click links or open attachments in those messages. According to the notice, no information leaks have turned up in the NURO fiber internet service or the company’s other services.
A major data breach hit Capcom on Oct. 22, 2026. Posts appearing on X described PlayStation Network users whose accounts were taken over and had unknown child accounts added to family groups without their permission. Some users said this took place even with multifactor authentication turned on and that the e-mail address connected to their account was changed. At the time of writing, Sony Interactive Entertainment had not confirmed a vulnerability, named a cause or issued a statement.
On Oct. 27, Sony reset the compromised email passwords in an effort to stop the damage from spreading. Customers affected by the breach need to set up new passwords using the So-net My Page portal. The company plans to contact affected customers one by one and has opened a dedicated phone line and an FAQ page for support.
Join the discussion