
Key facts
- Blueberry Pediatrics discovered on August 22, 2026 that an attacker exploited the vulnerability and copied patient data.
- Data taken from Blueberry Pediatrics covered names, birth dates, medical records, service dates, medical codes, service charges, and health plan names with policy numbers.
- The incident did not involve financial information or Social Security numbers.
- Because the same data surfaced in multiple incidents, certain affected people may receive multiple breach notices.
Blueberry Pediatrics said an attacker exposed sensitive data on 340,915 individuals after exploiting a vulnerability in the Metabase analytics platform, and the Mountain View, California-based company began notifying affected families by mail on Oct. 9, 2026.
The exposed information included names and birth dates along with medical records, service dates and medical codes. Service charges and health plan names with policy numbers were also taken. The company said no financial information or Social Security numbers were involved, and patient photos and videos were stored separately and were not compromised.
Blueberry Pediatrics, operated by SparkMD Inc., links families with board-certified pediatricians through telemedicine. The company, headquartered in Mountain View, California and dating to 2017, offers around-the-clock virtual pediatric visits and provides families with at-home medical kits. Carrot Fertility and Meridian Health Plan of Illinois are among its partners.
On August 22, 2026, Blueberry Pediatrics discovered that an attacker had exploited the vulnerability and obtained patient data. A separate public statement said the attacker first entered the company’s Metabase environment on Aug. 10, 2026 with administrator access. The company said it patched the flaw within hours of being notified, even though an intruder already had access to its data. After stopping the unauthorized access in roughly an hour, the company said its Metabase setup was running a non-vulnerable version.
Photon is a prescription service provider also used by Blueberry Pediatrics, and it exposed a subset of the same information. On August 24, 2026, Photon said another threat actor had exploited the same vulnerability and taken patient data. Data exposed through Photon included names and medication details, member IDs and addresses, plus phone numbers and email addresses. Intruders accessed Photon’s systems from Aug. 9, 2026, through Aug. 12, 2026, and the company patched on Aug. 21, 2026, with public disclosure on Oct. 8, 2026.
Dire Wolf claimed responsibility for the Photon breach on Aug. 19, 2026, saying it had stolen 63.3 GB of data. Photon and Blueberry Pediatrics have not confirmed Dire Wolf’s involvement and describe the perpetrators only as unknown actors. The cartel is financially motivated and was first observed in April/May 2025, and healthcare represents approximately 16% of its claimed victims.
The Metabase data analytics platform is used by more than 100,000 organizations. The flaw received a CVSS severity rating of 10.0, the highest score possible. Fixes were released by Metabase on Aug. 6, with the vendor saying under 3% of cloud customers were compromised before patching.
A public government record places the incident in Healthcare and Life Sciences and calls the initial attack type an inferred software vulnerability. The vendor’s investigation linked the broader episode to Aug. 3, when a cloud customer reported an API key — a code that programs use to communicate — created outside normal business hours.
Access was blocked right away, passwords and security protocols were updated after patches were applied, and a forensic cybersecurity firm was brought in by Blueberry Pediatrics. The company also tightened authentication controls, ran security reviews more often, added monitoring and escalation steps for vendor vulnerabilities, and contacted law enforcement. The HHS Office for Civil Rights breach portal does not include the incident.
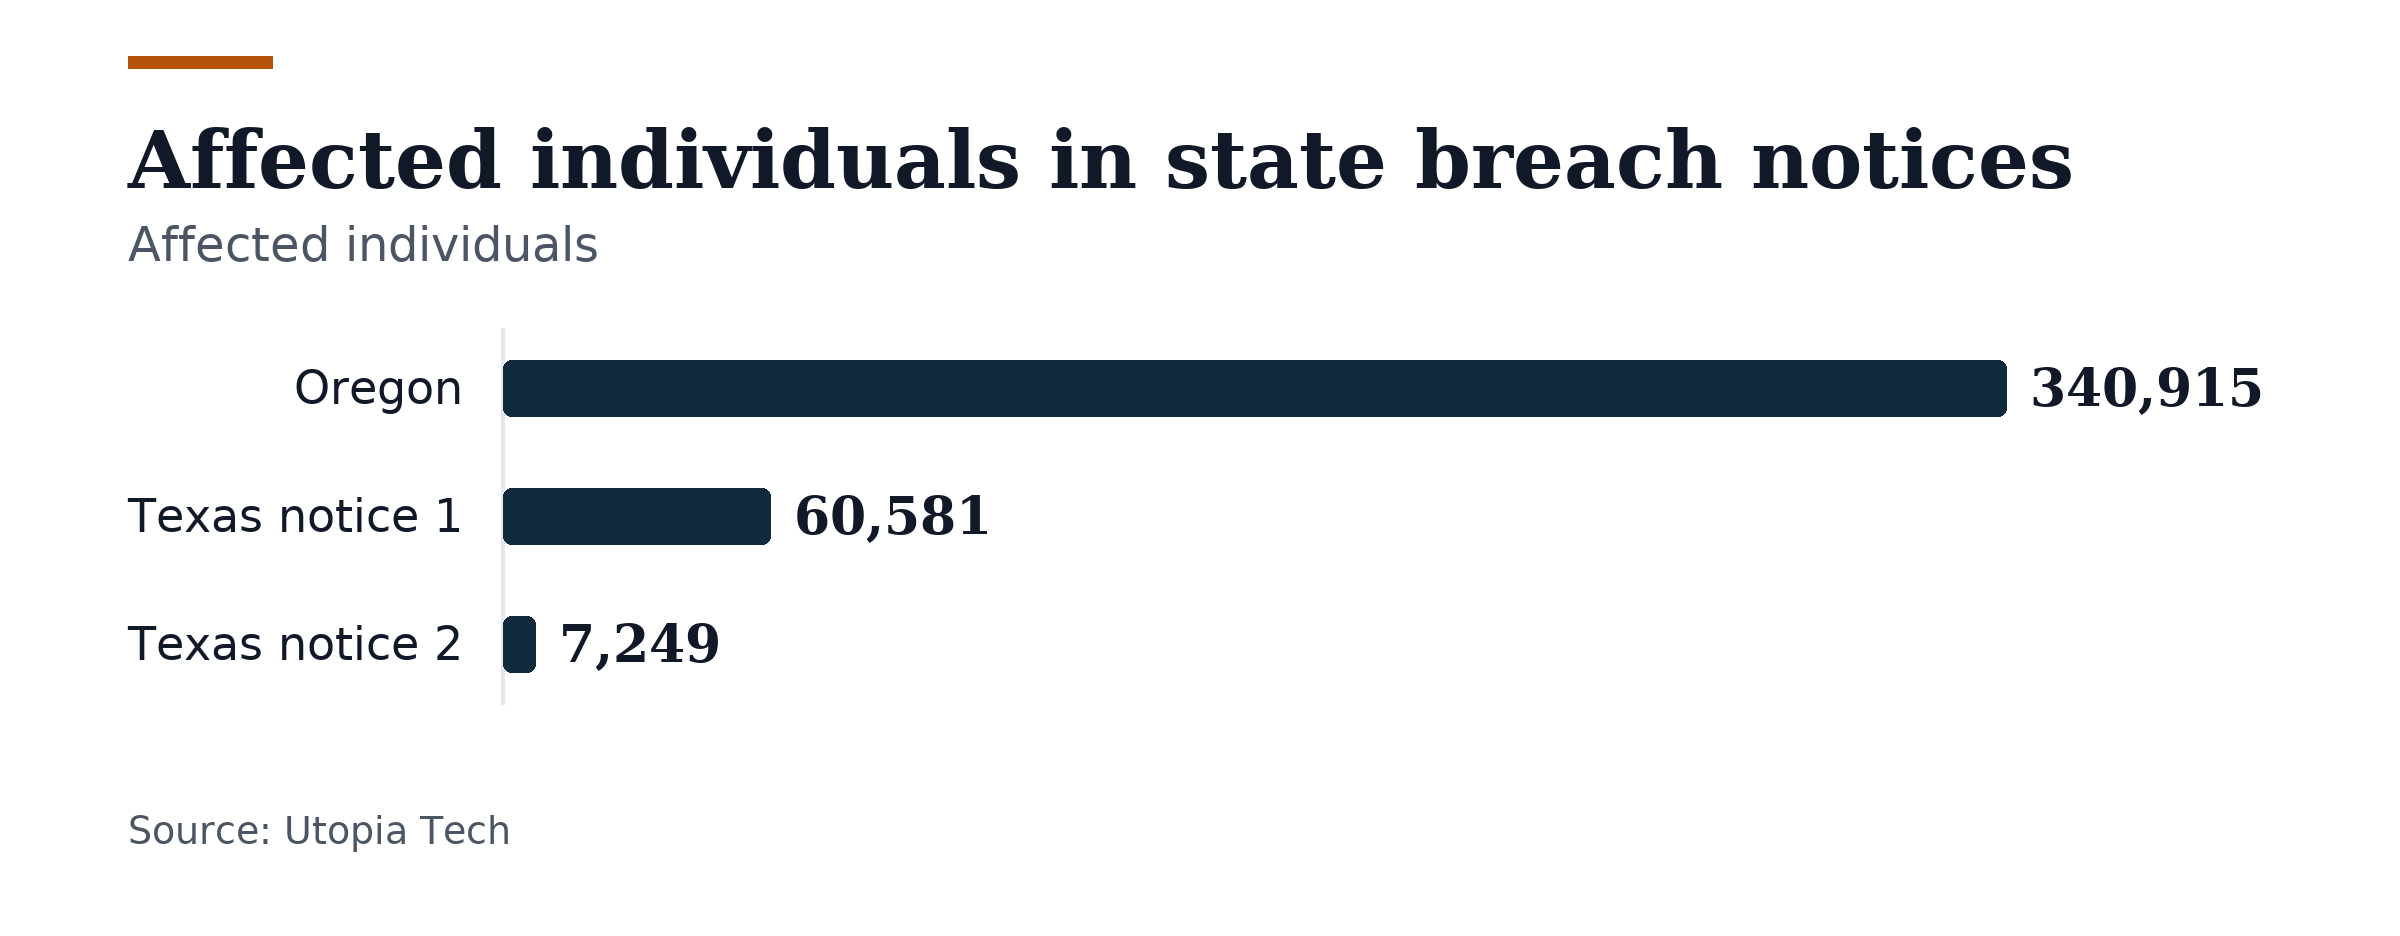
Oregon’s top prosecutor received notice that 340,915 individuals were affected, confirming the total scale with state regulators. Two breach notices went to Texas’ top prosecutor, covering 60,581 residents in one notice and 7,249 in the other. On Oct. 10, 2026, the breach was reported to the attorneys general of California and Oregon. California’s top prosecutor was told the breach involved patient names and medical records together with insurance information and contact details.
Affected families should review Explanation of Benefits statements and match them against actual visits and prescriptions to find unfamiliar entries. Parents should check children’s medical records for care or drugs that were never delivered, and they can request a fraud alert or credit freeze for a child’s credit file. When someone exploits health insurance information, it can lead to medical identity theft and may change a child’s medical record for years.
Young people typically lack a credit record, so criminals can use their personal information to open accounts without attracting notice. Because the same data surfaced in several incidents, certain affected people may receive several breach notices.
Legal teams are examining potential claims related to exposed personal and health information. Through Oct. 12, 2026, no lawsuits had surfaced that specifically name Blueberry Pediatrics. Blueberry Pediatrics recommends that families review account statements and credit reports. Families can direct questions to a help line at 888-752-8498 or to help@blueberrypediatrics.com.
Join the discussion