Key facts
- Four alleged members of a global ransomware syndicate were arrested by Ukrainian law enforcement working with the FBI.
- The organization is linked to ransom payments exceeding $40.5 million from at least 28 companies globally.
- Ukraine's National Police says the group targeted organizations in oil and gas, pharmaceuticals, manufacturing, logistics, finance, and critical infrastructure.
- Before attacks, the attackers looked at victim finances, assets, staff, and IT weaknesses, then stole data, encrypted systems, and demanded cryptocurrency payments.
The FBI and Ukrainian law enforcement arrested four suspects, BleepingComputer reported, describing them as alleged members of an international ransomware syndicate.
Ukrainian authorities carried out 66 simultaneous searches across Kyiv and 11 Ukrainian regions as part of a joint operation with U.S. law enforcement. Authorities took four suspected key members into custody, though the authorities did not reveal their exact arrest locations. Investigators took computers, mobile phones, bank cards, almost $370,000 in cash, and €20,000 during the searches.
A two-year investigation into a cybercrime organization of at least 27 individuals from Ukraine, Kazakhstan, Russia, and other countries preceded the arrests. Investigators say the organization linked to a larger cybercrime network of more than 60 members across eight jurisdictions, including former Conti ransomware gang members.
Ukraine’s National Police says the group targeted organizations in oil and gas, pharmaceuticals, manufacturing, logistics, finance, and critical infrastructure. Before launching attacks, the group reviewed victim finances, assets, staffing, and IT vulnerabilities, then stole data, encrypted systems, and demanded cryptocurrency payments.
Maksym Tsutskiridze, the acting National Police chief, said investigators identified at least 28 companies that paid ransoms totaling more than $40.5 million. Tsutskiridze said the ransom total was about UAH 1.8 billion.
He said victims had already paid the money and investigators were still establishing the full extent of the damage. Ukrainian authorities say the investigation continues as police work to identify more members of the international network and their role in other cyber attacks.
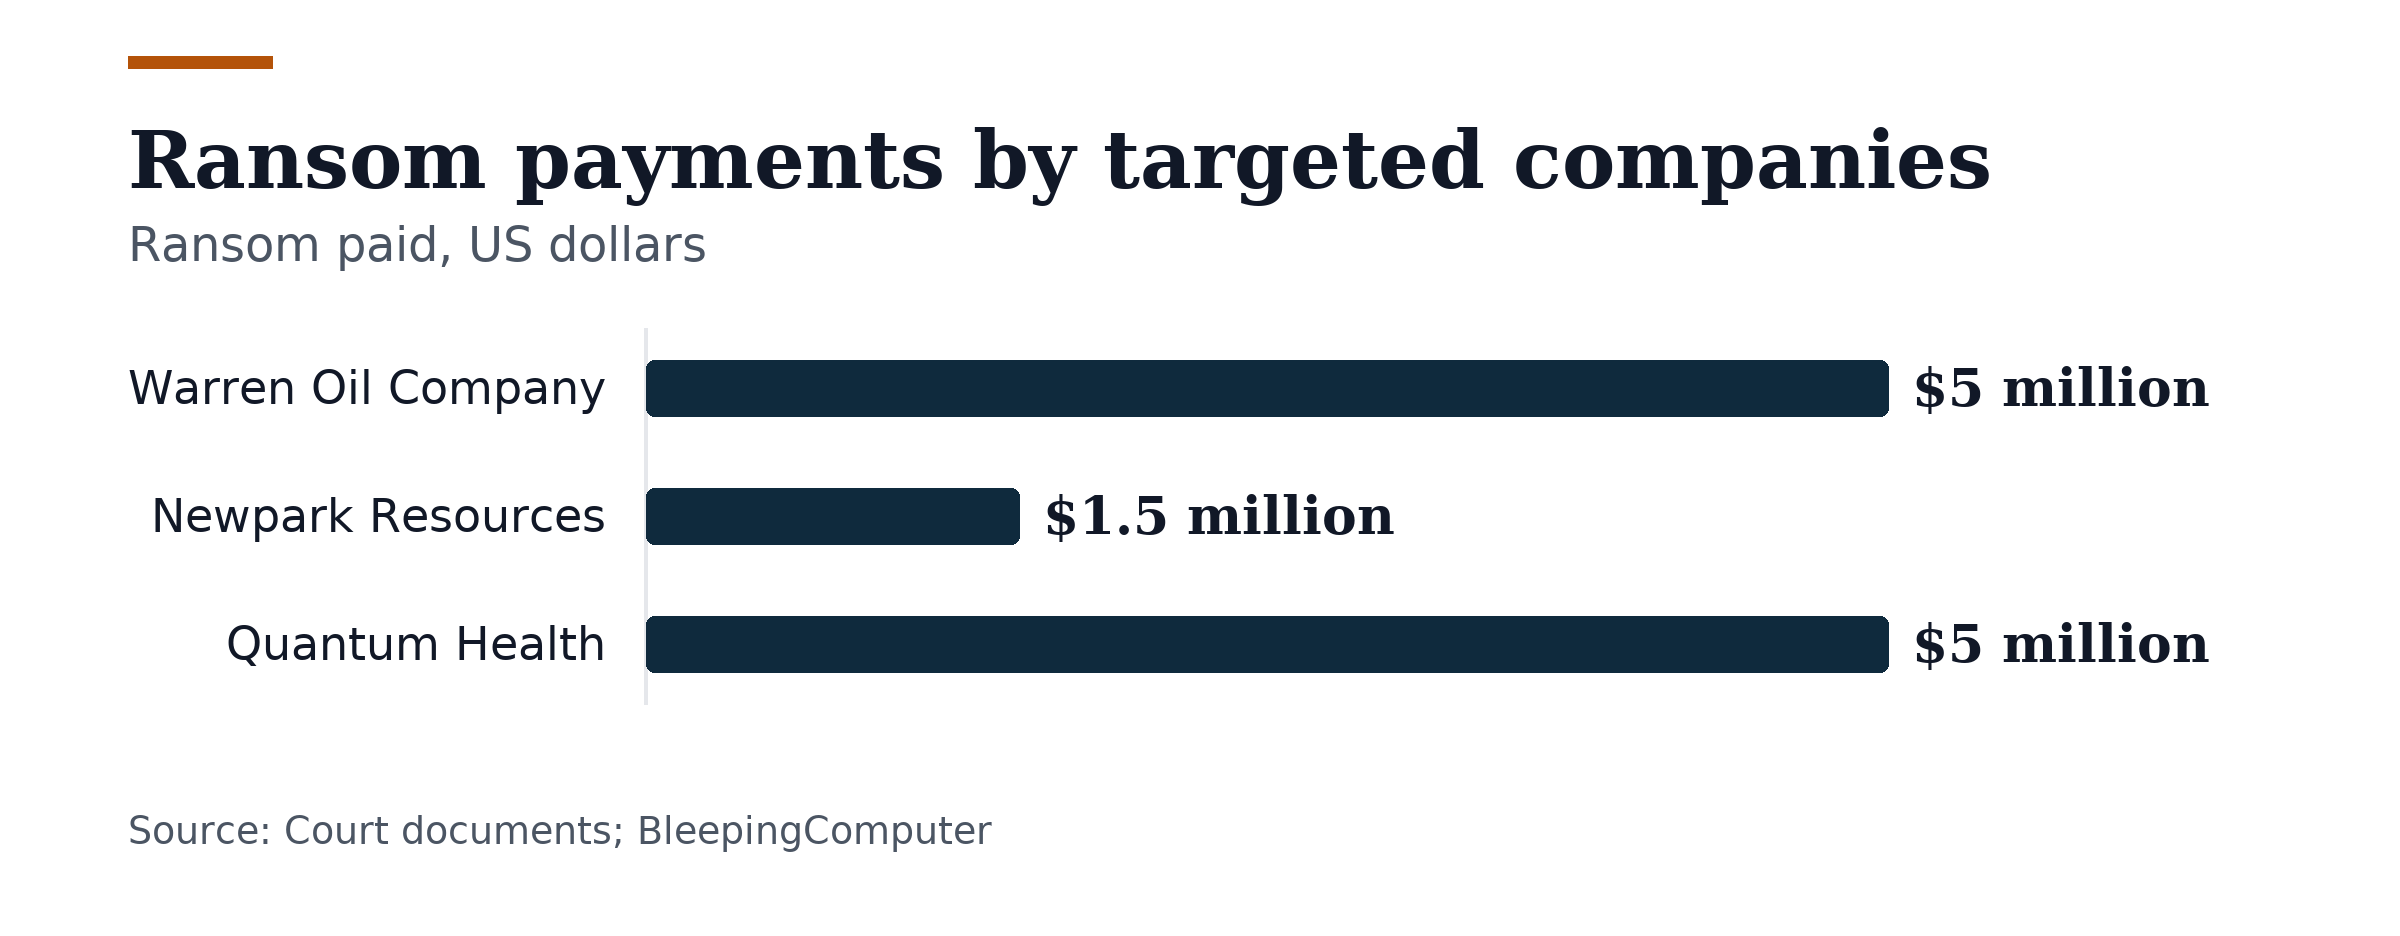
Court records identify victims including Warren Oil Company, Maxxis International-USA, Newpark Resources, and Quantum Health. Court documents say hackers copied 1.4 TB of data during an August 2024 attack on Warren Oil Company, and the attackers received an 84.5 BTC ransom payment worth about $5 million at the time.
Court records allege Newpark Resources paid $1.5 million in December 2024. Court records allege Quantum Health paid $5 million in June 2026 after an initial $15 million ransom demand. In another case, attackers initially demanded $10 million but received $5 million after negotiations.
LeMagIT reported that BlackSuit claimed Maxxis International was a victim in November 2024. Authorities have not called the four arrested suspects former Conti members or confirmed ties to BlackSuit or Chaos.
Ukrainian court records connect Chaos to the criminal organization as the ransomware involved. Court records say the Conti ransomware operation shut down in May 2022, and its members dispersed into smaller ransomware gangs and other cybercrime operations.
Court records say BlackSuit, linked to former Conti members, first operated as Quantum ransomware in January 2022 before becoming Royal. Royal started using the BlackSuit name in June 2023 after testing a new encryptor, and Royal carried out high-profile attacks under the BlackSuit name, including an attack on the City of Dallas, Texas.
Court records say criminals posed as IT support staff and entered corporate networks through a custom system that generated AI voice messages for fraudulent calls. During the calls, they tricked employees into revealing login credentials or installing remote-access software, letting attackers enter internal corporate systems.
An attacker kept an employee on the phone while a second attacker entered the company’s systems, court records describe. The call did not end until the attackers confirmed the intrusion had succeeded.
Tsutskiridze said the group created a platform with AI-generated voice messages. Tsutskiridze said the group called employees posing as IT support and convinced them to share credentials or install remote-access software. “They created their own platform featuring voice messages generated by artificial intelligence.”
Court records say the attackers used remote-access tools including TeamViewer and AnyDesk, spoofed phone numbers, and phishing pages that impersonated corporate virtual private network (VPN) services. During the Warren Oil Company attack, attackers fooled an employee into typing credentials on a fake VPN page, court records allege. The attackers then got a multifactor authentication code to enter the corporate network.
After gaining access, the attackers stole sensitive information, encrypted files using ransomware, and disrupted operations at the victim, court records say. The gang demanded cryptocurrency payments to restore access to encrypted systems and threatened to release stolen corporate data publicly.
Tsutskiridze said the group blocked companies from their data and demanded millions to decrypt it. Tsutskiridze said the group threatened to publish stolen information and pressured victims into paying cryptocurrency ransoms.
Four alleged key members received formal suspicion notices and remain in custody. Prosecutors charged the suspects under Ukrainian law with belonging to a criminal organization and illegally interfering with information systems. If convicted, the suspects face up to 15 years in prison.
The National Police released a video with investigation footage, including raids, seized cash, investigator interviews, and investigators questioning a suspect. The video includes audio from an alleged extortion call demanding $15 million and claiming theft of over 1.5 TB of corporate data.
Join the discussion