Key facts
- The companies will pay at least $300,000 in penalties and costs to the coalition of states.
- Hackers entered PJ&A's systems in March 2023 using a PJ&A Coding employee's credentials.
- The companies must set rules for collecting, using, storing, and destroying personal health information.
- New York will receive $100,000 of the initial payment for penalties and costs.
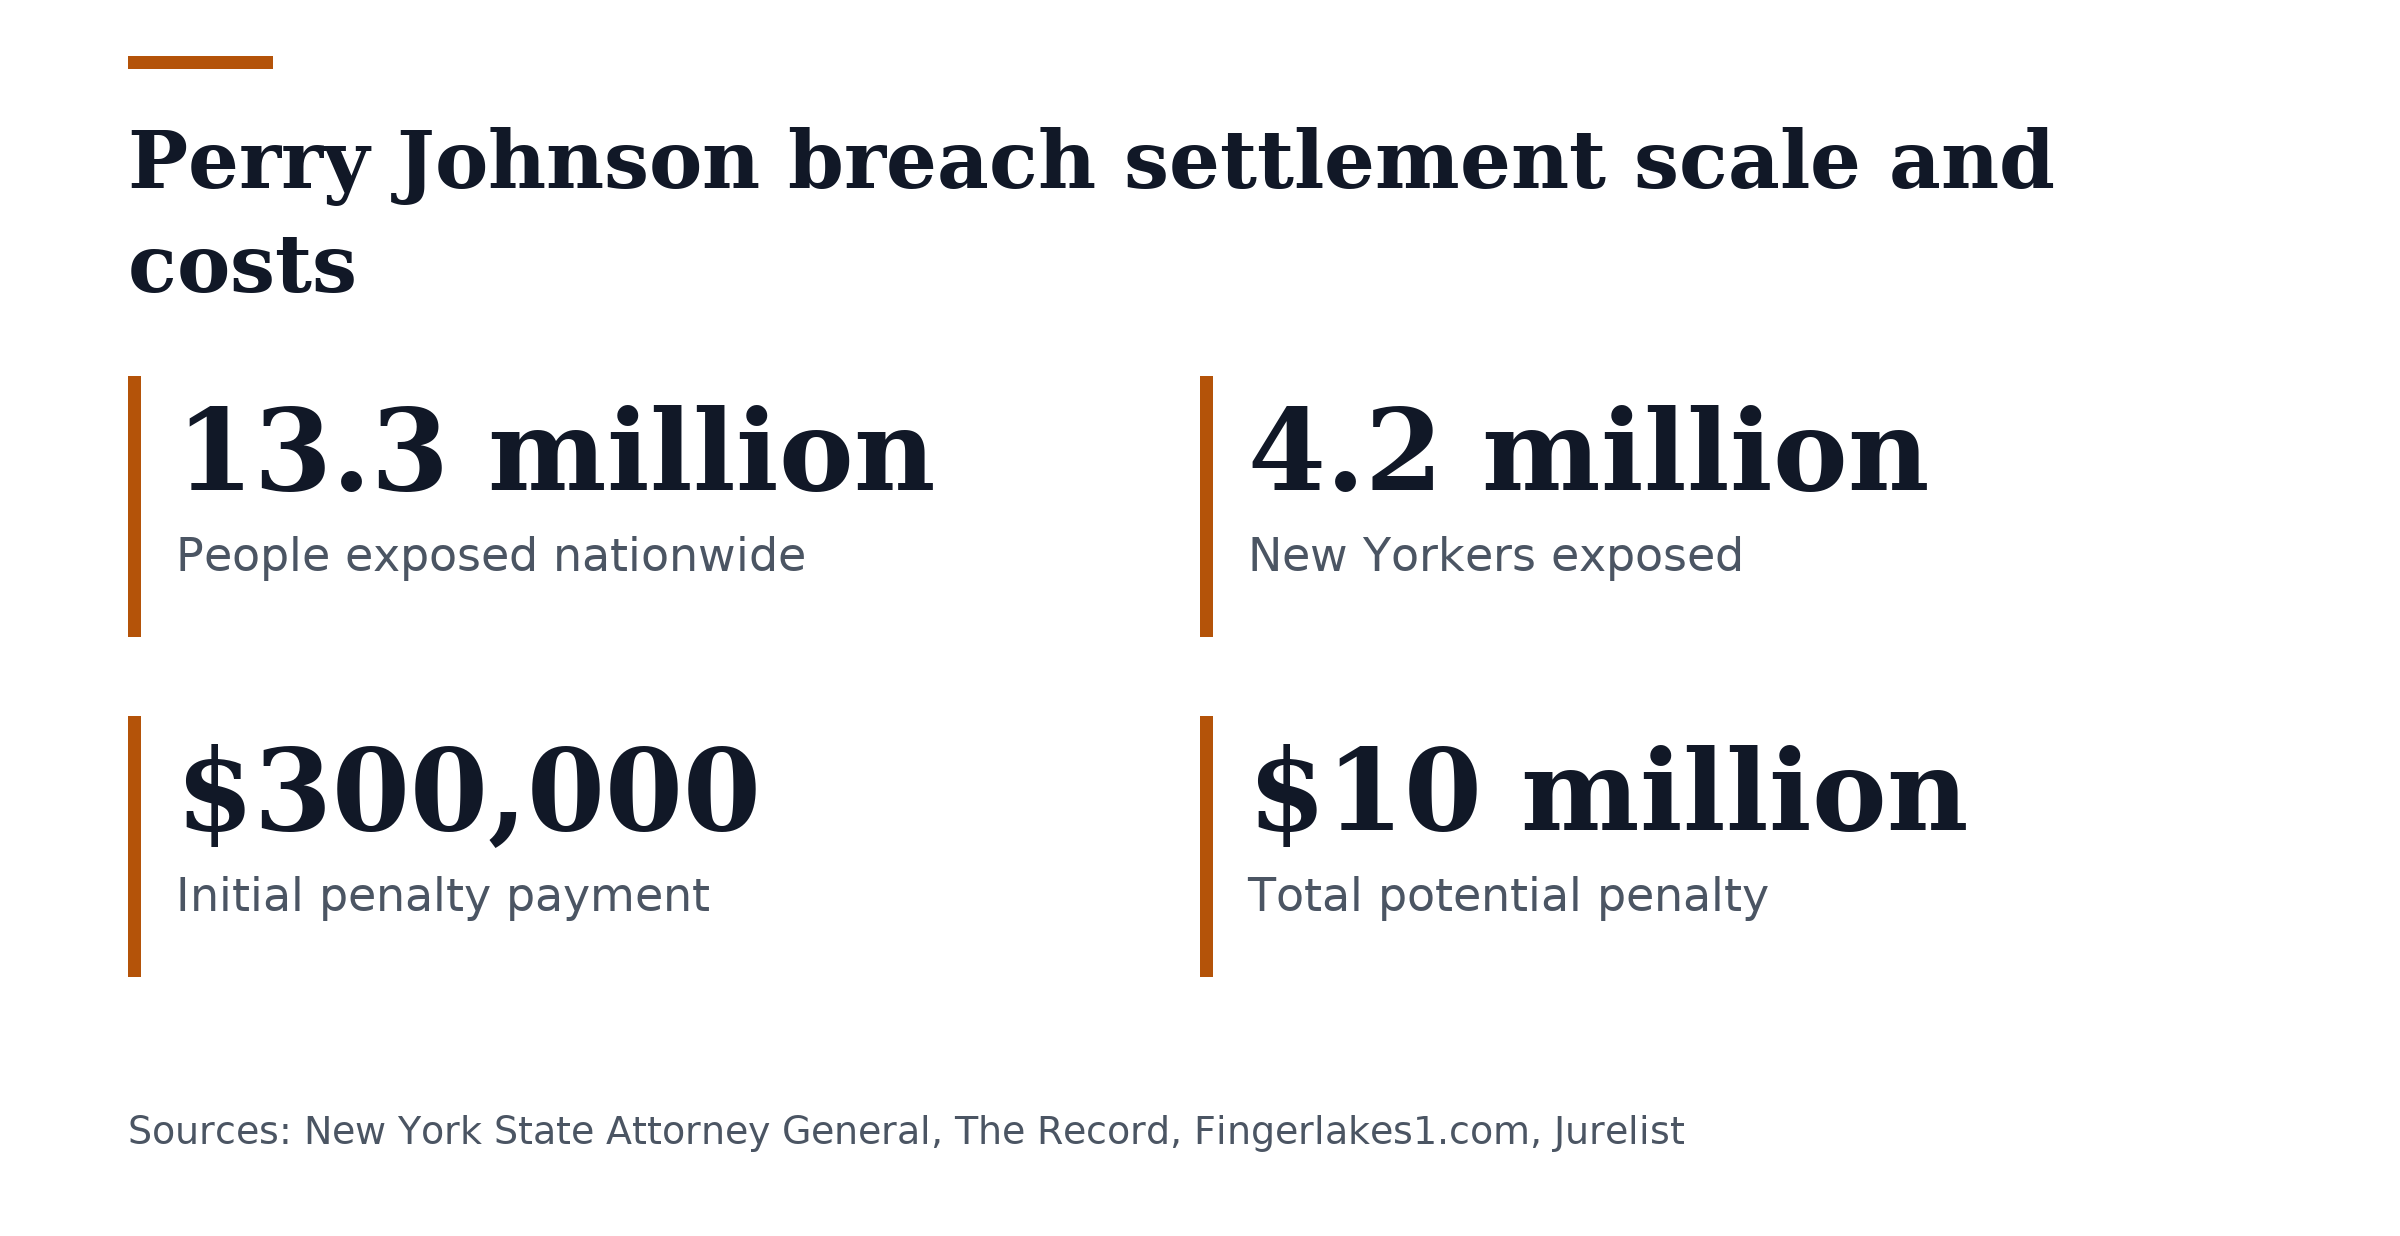
On Nov. 6, 2026, New York Attorney General Letitia James and her counterparts in Connecticut, Michigan and New Jersey reached a settlement with five Perry Johnson companies over a March 2023 breach that exposed personal information belonging to more than 13.3 million people across the country, including about 4.2 million in New York.
The settlement covers five companies: Perry Johnson & Associates Inc. (PJ&A), Perry Johnson Inc. (PJI), Perry Johnson & Associates Coding Inc., Perry Johnson & Associates Radiology Inc., and Medical Transcription and Coding Inc. PJ&A worked as an information technology vendor for health care organizations nationwide, including in New York, handling coding, billing and recording.
A PJ&A Coding employee’s credentials gave hackers entry to PJ&A’s systems in March 2023. Remote access did not require multifactor authentication at the time of the intrusion. Over the months that followed, the attackers collected passwords and read unencrypted files containing personal and protected health information. PJI security software logged the intruders’ activity but was not configured to alert security staff.
The company found out only after the hackers reached out, about two months after they first entered. Exposed records included names, birth dates and diagnoses. Insurance information, home addresses, Social Security numbers and hospital account numbers were also exposed. Medical transcription files also contained lab results, diagnostic test results and medication names.
The coalition of states will receive at least $300,000 from the companies for penalties and costs. New York will get $100,000 of the initial payment. The states call the payment penalties and costs, not compensation for people affected by the breach. Violating the agreement would require the firms to pay an additional $9.7 million to the states, for a possible total reaching $10 million.
The agreement requires an information-security program and an incident-response plan. The firms must use multifactor login, manage passwords, protect data and track assets. Yearly risk assessments in line with HIPAA are required. The firms must also set rules for how they collect, use, store and destroy personal health information.
“Your health is your business, and companies entrusted with personal health information have a duty to rigorously protect it,” said Attorney General James. Jordan Adler, senior enforcement counsel, handled the New York matter from the Bureau of Internet and Technology. Bureau Chief Kim Berger and Deputy Bureau Chief Clark Russell supervised that work. The bureau sits inside the Division for Economic Justice, led by Chief Deputy Attorney General Chris D’Angelo and overseen by First Deputy Attorney General Meghan Faux.
The company gave no response to a request for comment. State attorneys general filed suit against the medical transcription, coding and imaging subsidiaries of the Nevada-based Perry Johnson Companies.
Join the discussion