
Key facts
- Google committed to give an update on the reworked program in the first quarter of 2027. It has not said what controls it will introduce.
- The pause does not cover OSS VRP supply chain reports, reports submitted before October 1, 2026, or outstanding reports.
- The OSS VRP launched in August 2022 with rewards of $100 to $31,337. It covers Google-maintained open source projects such as Golang, Angular, Bazel, Protocol Buffers and Fuchsia, plus repository settings.
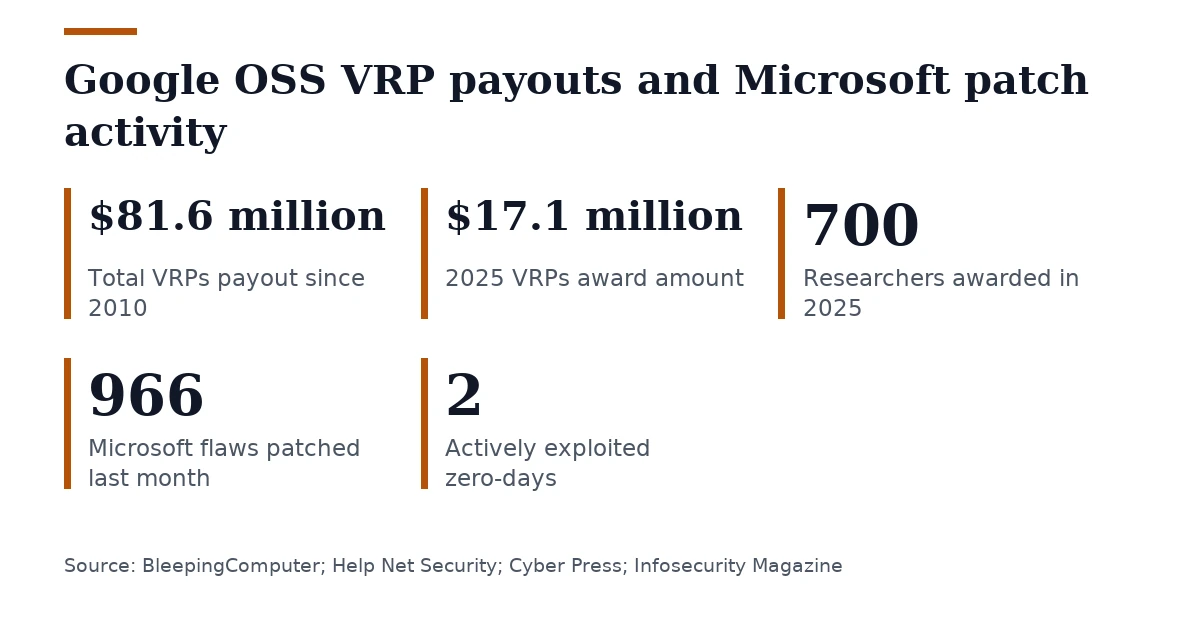
- Google's VRPs have paid over $81.6 million since 2010. In 2025 Google awarded a record $17.1 million to more than 700 researchers, up 40% from $12 million in 2024.
Google stopped accepting new product vulnerability submissions to its Open Source Software Vulnerability Rewards Program (OSS VRP) as of Oct. 1, 2026, according to TechCrunch. BleepingComputer and Help Net Security report the same cutoff.
This pause is due to a significant rise in automated submissions, the vast majority of which are not valid.
Google, BleepingComputer
Google describes the flood as automated. It has not, in the reports cited here, said that AI generated the submissions. BleepingComputer ties the pause to an AI spam surge and notes that other programs have also faced AI-generated reports.
Google has committed to give an update on the reworked program in the first quarter of 2027, TechCrunch reported. It has not said what controls it will introduce.
What the pause means for researchers
The pause does not cover OSS VRP supply chain reports, reports submitted before Oct. 1, 2026, or outstanding reports, according to BleepingComputer. Infosecurity Magazine, Help Net Security and Cyber Press describe the same exclusions.
Under that description, a researcher who filed before the cutoff still has a report in the program’s queue. A researcher with a new product vulnerability finding has no OSS VRP intake until Google reworks the program, while supply chain reports remain open.
Google directs researchers to two other programs, BleepingComputer reports. The Patch Rewards Program pays up to $15,000 for high-impact fixes, and the Cloud VRP covers Google Cloud repositories that affect Cloud products. Help Net Security and Cyber Press describe the same alternatives.
A vulnerability rewards program, or VRP, pays researchers who privately report flaws to a vendor so the vendor can fix the flaws before details become public.
A program with a five-figure ceiling
The OSS VRP launched in August 2022 with rewards of $100 to $31,337, BleepingComputer reported. According to Infosecurity Magazine, the program covers Google-maintained open source projects such as Golang, Angular, Bazel, Protocol Buffers and Fuchsia, plus repository settings.
Google’s wider rewards effort has been growing, BleepingComputer reported. Its VRPs have paid more than $81.6 million since 2010. In 2025 Google awarded a record $17.1 million to more than 700 researchers, up 40% from $12 million in 2024.
An earlier tightening, March 2026
The freeze followed a narrower step. Cyber Press and EVTV Miami report that Google tightened OSS VRP rules in March 2026 after seeing reports with hallucinated triggers and theoretical issues. A hallucinated trigger is an invented way to make a bug happen that does not work when tested.
Under those rules, certain memory-corruption reports in high-priority projects required exact OSS-Fuzz reproduction steps or a merged patch, according to the same reports. OSS-Fuzz is Google’s continuous fuzzing service, which feeds programs unexpected input to find crashes.
Other programs report similar pressure
BleepingComputer reports that in January the curl maintainer ended the project’s HackerOne bounty. It also reports that in mid-September Intel removed financial rewards on its Intigriti program without explaining why.
EVTV Miami reports that GitHub said in May that AI had made it easier to start security research and that submission volumes across the industry had grown sharply. EVTV Miami also reports that Microsoft warned that month that AI-driven discovery would raise operational demands industry-wide.
Why it matters
Bug bounties rest on a trade: researchers do work up front, and vendors triage reports and pay for valid ones. By Google’s account, most of the automated submissions it received are not valid.
The pressure Google describes is not limited to its own program. BleepingComputer reports that curl and Intel changed their programs, and EVTV Miami attributes to GitHub and Microsoft the view that AI is raising submission volumes and workload across the industry.
What to watch next
- What Google's first-quarter 2027 update contains, since the company has not said what controls it will add (TechCrunch).
- Whether Google's Patch Rewards Program and Cloud VRP, which it points researchers toward, change how they handle submissions (BleepingComputer).
- Whether other programs follow Intel, which removed financial rewards in mid-September without explanation (BleepingComputer).
Join the discussion