
Key facts
- NEAR AI says an attacker exploited an SGLang remote code execution vulnerability to run code on one inference server on Nov. 8, 2026.
- NEAR AI said the protected environment cannot defend against flaws in the software operating inside it.
- SGLang ran inside the trusted execution environment, which let the attacker reach confidential requests there, according to NEAR AI.
- The exposed records contained names and email addresses, with plan and balance details for some accounts.
NEAR AI says an attacker exploited an SGLang remote code execution vulnerability to run code on one inference server. The intrusion occurred on Nov. 8, 2026, and the attacker could have viewed requests processed there, including confidential-mode traffic.
NEAR AI says the intruder reached an internal system tied to Private Chat, a product it had already retired, and downloaded account details for about 100 users. Those records held names and email addresses, with plan and balance details for some accounts. The balance means credit for the AI service, not a wallet address or key.
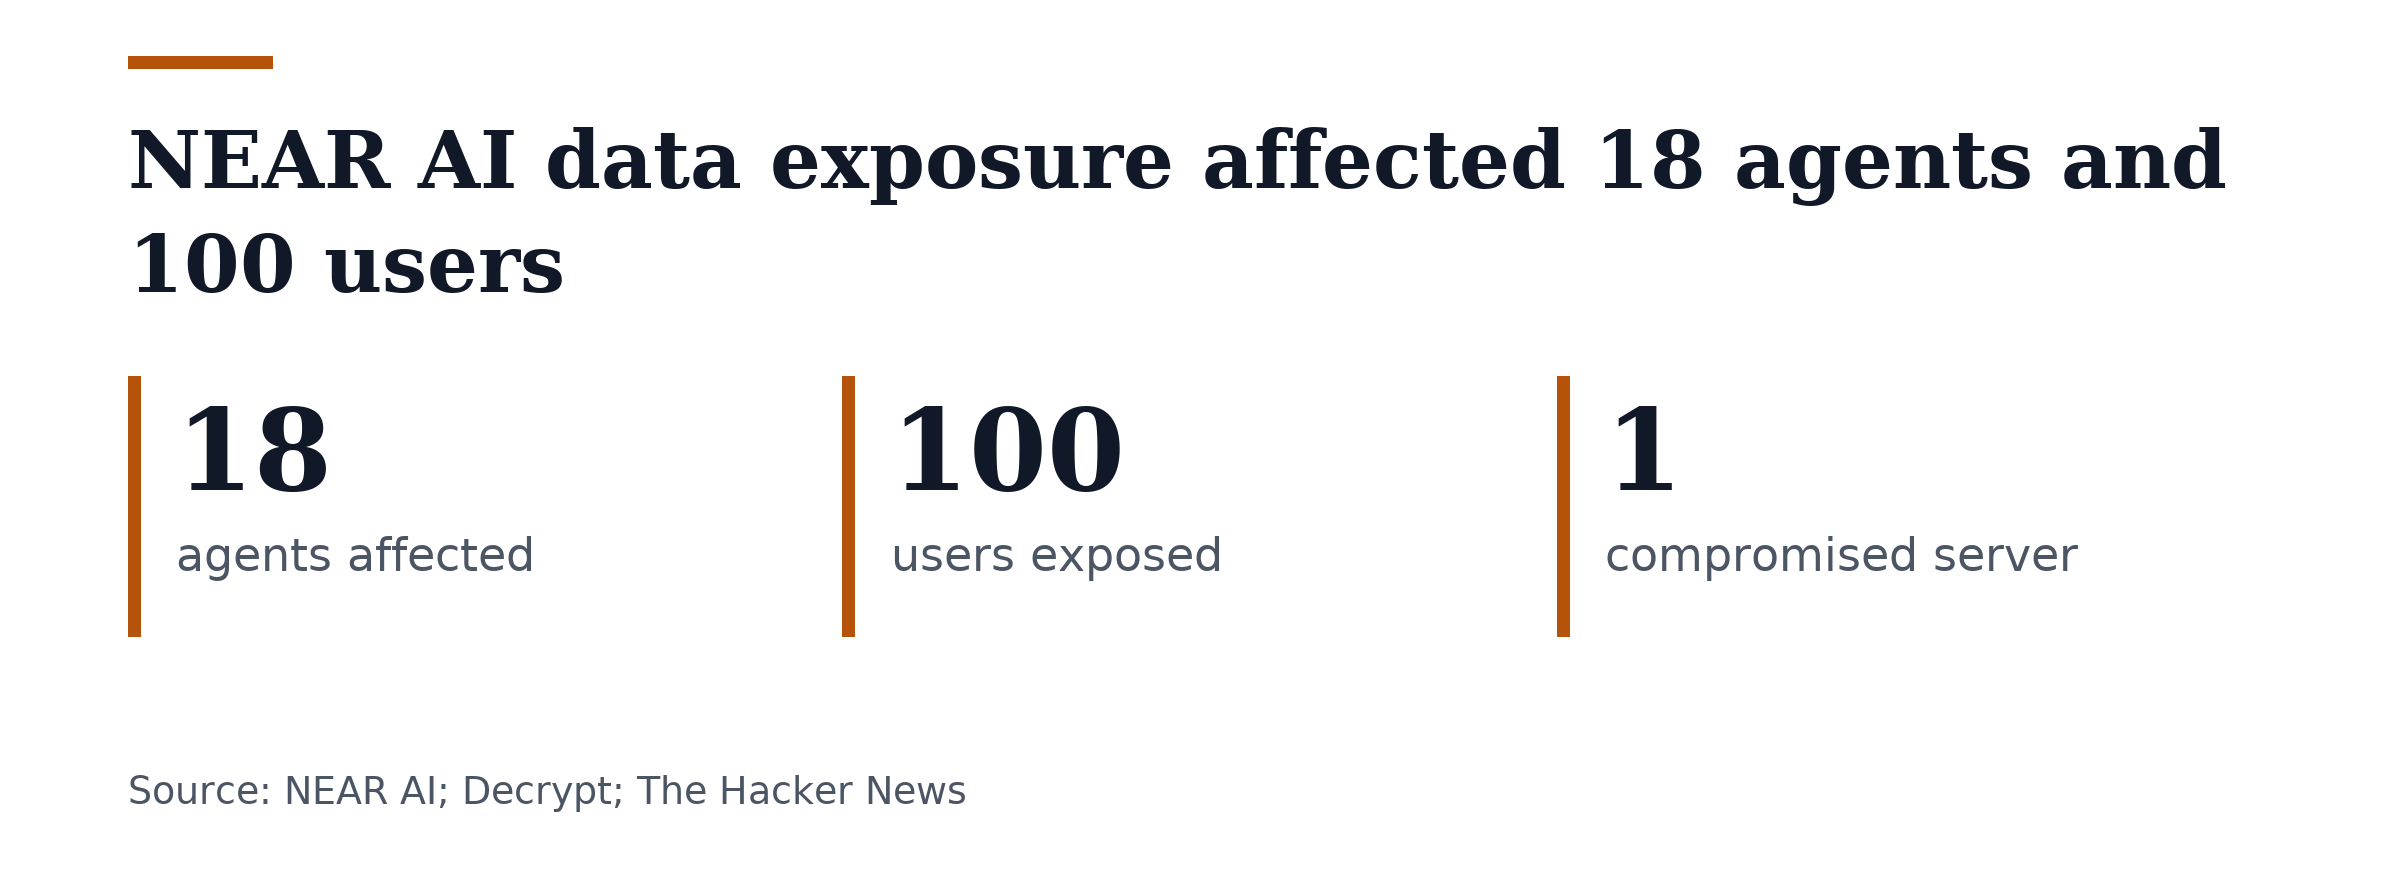
On an older NEAR AI Agents deployment outside the trusted execution environment, the attacker reached 18 agents and took chat history, settings and logs from them, NEAR AI says. The company reached out to every owner of the 18 affected agents individually.
Logs from those agents exposed NEAR AI Cloud API keys for two customers, and the company revoked both, NEAR AI says. The company has not said whether the intruder used either key.
Confidential mode handles requests inside a protected execution area designed so the company cannot see them, NEAR AI says. But SGLang ran inside the trusted execution environment, allowing the attacker to reach confidential requests there, the company said. “does not protect against a vulnerability in the software running inside the environment,” NEAR AI said.
Investigators saw no evidence of access to stored Private Chat conversations or files, NEAR AI says. The company gave no count of confidential requests that attackers might have observed on the compromised server.
SGLang is open-source software designed to run AI models and produce responses to user requests. Inference is the step where a trained model produces an answer. It loads an AI model into graphics-card memory, distributes requests, and delivers answers. If an attacker runs code on the server, the inference engine sees each request in plain text while the model processes it, exposing confidential data.
Carnegie Mellon University’s CERT Coordination Center documented six vulnerabilities in SGLang in July. Researchers said certain flaws in SGLang might allow command execution or credential exposure depending on how the server is set up. NEAR AI did not identify the exploited flaw by CVE number or name affected SGLang versions, meaning the breach cannot be linked to earlier SGLang disclosures.
Jasnah Inc. operates NEAR AI, which sells private AI computing power. NEAR AI said NEAR Protocol and other NEAR services were not affected by the breach. The company said attackers went after the AI service instead of the NEAR Protocol blockchain, so they took no cryptocurrency, wallets or private keys. NEAR AI said its confidential inference stack remains publicly visible so outside parties can verify what runs inside it.
On October 15, Brave said its Leo assistant uses the GLM 5.3 Flash model for chats inside a trusted execution environment run by NEAR AI. The company has not said whether the affected server handled any chats for Brave’s Leo assistant.
After detecting the intrusion, NEAR AI canceled all active sessions and administrative credentials. NEAR AI engineers patched the SGLang flaw on every inference server and rotated remaining credentials. NEAR AI completed a full forensic review. The Crypto Times says NEAR AI temporarily suspended cloud inference after confirming unauthorized access and later brought the service back.
The company replaced every agent token and shut down Private Chat. Users whose account details or agents were confirmed accessed received word from NEAR AI at security@near.ai. The company said no action is needed from anyone it has not contacted.
Users should watch for unexpected messages about their account or balance, NEAR AI says. NEAR AI said it will send any required regulatory notifications. The company has not said whether it contacted people whose requests passed through the affected server on Nov. 8.
Decrypt and Bitcoin News date NEAR AI’s incident report to November 9, 2026, while The Crypto Times dates it to November 10, 2026. The Crypto Times says NEAR AI revealed the breach early on November 10, halted cloud inference, and later restored it.
The company informed the SGLang project about the flaw but has not said whether SGLang released a fix. NEAR AI also said its security review would examine inference software and surrounding services with the same rigor applied to protected computing environments.
Join the discussion