Key facts
- AOMEI Technology’s update and notification infrastructure was compromised between April and July 2026, allowing attackers to push malware through AOMEI Backupper’s update mechanism.
- Attackers altered two configuration files—down_html.ini and Notifycfg.ini—on AOMEI’s servers to redirect AOMEI Backupper to download a malicious ZIP archive instead of legitimate updates.
- The malicious ZIP archive contained CROSSROAD, a downloader that installed a persistent remote-access backdoor (SHINYROAD) alongside legitimate Radmin software.
- AOMEI Backupper’s update mechanism does not cryptographically verify the down_html.ini or Notifycfg.ini files, allowing attackers to manipulate them undetected.
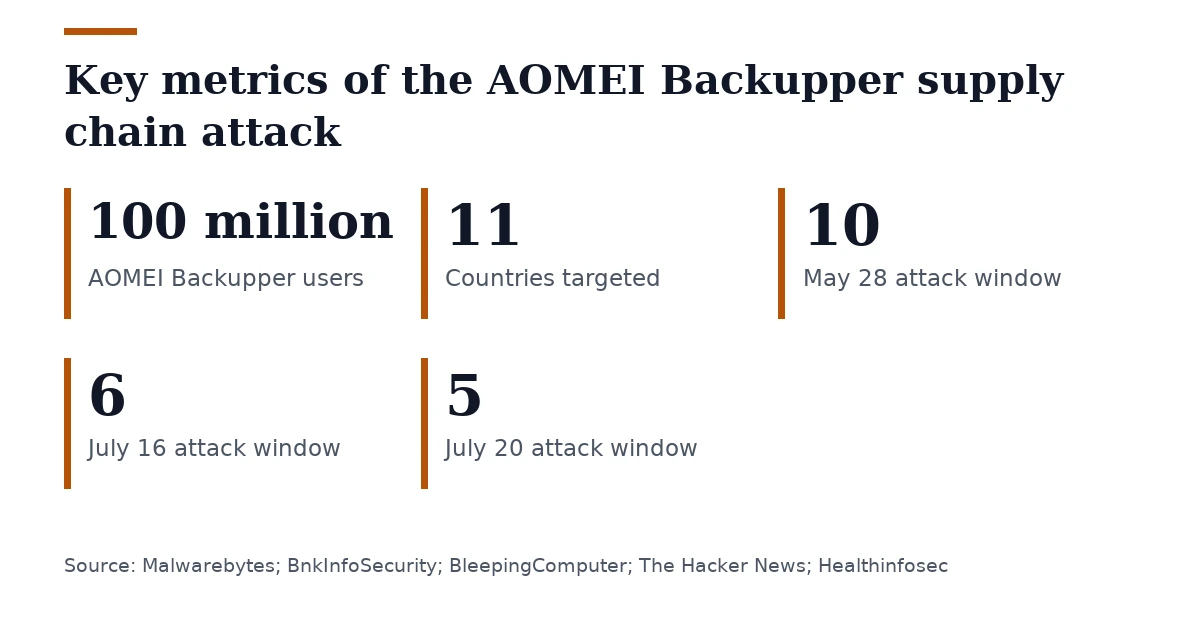
Attackers compromised AOMEI Technology’s update and notification infrastructure between April and July 2026, exploiting AOMEI Backupper’s update mechanism to distribute malware without requiring software vulnerabilities or user interaction. The threat actor, tracked as UNC7017 according to BnkInfoSecurity, targeted organizations in 11 countries, including the US, Australia, India, Spain, and Switzerland, across sectors like IT, telecommunications, and higher education. Over 100 million users worldwide use AOMEI Backupper, including major companies such as Amazon, Microsoft, Cisco, and Walmart. The malware installed a persistent remote-access backdoor (SHINYROAD) alongside legitimate Radmin software.
The attack occurred in three confirmed windows: May 28, 2026 (10 minutes), July 16, 2026 (six minutes), and July 20, 2026 (five minutes), after which the files reverted to legitimate versions. The short exposure windows made detection difficult, as the files reverted to legitimate versions shortly after tampering. The attack represents a new trend in supply-chain compromises: ephemeral configuration tampering with short exposure windows, avoiding traditional detection methods. AOMEI Technology secured its servers by the end of July 2026, but this does not remove malware already installed on compromised endpoints.
Attackers altered two configuration files—down_html.ini and Notifycfg.ini—on AOMEI’s servers to redirect AOMEI Backupper to download a malicious ZIP archive instead of legitimate updates. Attackers modified the files to include a malicious download URL and a matching checksum, bypassing the software’s verification.
AOMEI Backupper’s update mechanism does not cryptographically verify these configuration files, allowing attackers to manipulate them undetected. This design flaw enabled the supply-chain attack without exploiting software vulnerabilities.
The malicious ZIP archive contained CROSSROAD, a downloader that installed a persistent remote-access backdoor (SHINYROAD) alongside legitimate Radmin software. SHINYROAD used DLL search-order hijacking (a technique where placing a malicious DLL in a location where a legitimate application looks for it causes the malicious code to execute under the guise of a trusted process) to load malicious code into a legitimate Windows process, evading detection. The malware (CROSSROAD) checked the infected machine’s geolocation and aborted execution if the country code was CN (China). The attackers also exploited AnyViewer, AOMEI’s remote-access tool, using the same compromised update infrastructure, though no one reported confirmed infections for it.
On July 20, 2026, attackers used a WebDAV trick (a method that uses the Web Distributed Authoring and Versioning protocol to force a connection) to steal NetNTLMv2 authentication hashes (a Windows credential) from infected machines by forcing an invisible pop-up to connect to an attacker-controlled server. This technique required no code execution, making it harder to detect. The attack infrastructure shifted from Alibaba Cloud Object Storage (April–May 2026) to storage-data.com and Google Cloud Storage (July 2026), complicating blocking efforts. The attackers used storage-data.com, promotion.storage-data.com, and aomei.storage-data.com for command-and-control (C2) communications and payload delivery.
The malware downloader (CROSSROAD) deletes itself after staging the backdoor, complicating forensic analysis. Victims can check for compromise by looking for a scheduled task named RadminComponentRuntime or unexpected files like upgrade-now.exe in AOMEI Backupper’s installation folders. Blocking the domains used for C2 communications (storage-data.com, promotion.storage-data.com, and aomei.storage-data.com) can disrupt the attackers’ control over infected systems. AOMEI Technology’s CTO is leading an internal investigation into the breach, but the company has not confirmed how attackers gained access to its servers.
ManageEngine’s Threat Analysis Lab first detected the attack on May 28, 2026, when AOMEI Backupper installed Radmin on two unrelated endpoints. The lab notified AOMEI on June 7, 2026, but the company initially dismissed the possibility of server-side compromise.
Join the discussion